Encryption, TLS, and Cryptography Deep Dive
Start here: the basics in plain words
When your browser talks to your bank, the data crosses Wi-Fi, your ISP and several networks you don't control. Anyone along that path could read or change it. Cryptography solves three problems: keeping the data secret, proving it wasn't changed, and proving who you're talking to. TLS (Transport Layer Security) is the protocol that combines these tools to protect web traffic. It is the "S" in HTTPS and the padlock in the browser.
An analogy that maps onto the real pieces:
- Symmetric encryption is a box with one key. Whoever has a copy of the key can lock and unlock it. It is fast, but both sides need the same key first.
- Asymmetric encryption is a padlock you hand out freely (the public key) and a key only you keep (the private key). Anyone can click the padlock shut on a message, but only you can open it. It solves "how do we agree on a shared key with a stranger", but it is slow.
- A hash is a fingerprint of the data. Change one letter and the fingerprint changes completely, and you can't rebuild the data from the fingerprint.
- A certificate is an ID card for a server: "this public key belongs to
bank.com", signed by a Certificate Authority (CA) that your browser already trusts.
TLS uses them in that order. Asymmetric cryptography and the certificate prove who the server is and agree a fresh shared key. Then fast symmetric encryption protects the rest of the conversation.
The readable data, and the scrambled version that's safe to send.
The secret value that controls the scrambling. Security depends on keeping keys secret, not on hiding the algorithm.
The first few messages of a TLS connection, where the two sides prove identity and agree keys before any real data flows.
The named combination of algorithms a connection uses, e.g. TLS_AES_128_GCM_SHA256.
An organisation trusted to sign certificates. If a CA signs a certificate for the wrong person, that person can impersonate the site.
Memory hook"padlock to meet, shared box to talk". Asymmetric crypto is for introductions and identity; symmetric crypto carries the actual conversation.
Abbreviations Decoded
Cryptography is drowning in acronyms. Each is expanded again where it first matters below, but this is the one place to look one up. Grouped by job:
Encryption and modes
Advanced Encryption Standard. The worldwide default symmetric cipher, chosen by NIST in 2001.
National Institute of Standards and Technology, the US agency that publishes most cryptographic standards (FIPS, SP 800 series).
Federal Information Processing Standard, a NIST standard US government systems must follow (e.g. FIPS 197 = AES).
Electronic Codebook / Cipher Block Chaining / Counter: ways of applying a block cipher to data longer than one block.
Galois/Counter Mode: counter-mode encryption plus a GHASH authentication tag. Named after the Galois-field maths used for the tag.
Counter with CBC-MAC: counter-mode encryption plus a CBC-based MAC. Used in Wi-Fi (WPA2's CCMP) and IoT.
Synthetic Initialization Vector: a mode that derives the IV from the message, so accidental nonce reuse is far less harmful.
XEX-based Tweaked-codebook mode with ciphertext Stealing: the disk-encryption mode (BitLocker, FileVault, LUKS). Encrypts, doesn't authenticate.
Authenticated Encryption with Associated Data: one operation that encrypts and detects tampering. AES-GCM and ChaCha20-Poly1305 are AEADs.
Additional Authenticated Data: bytes that are protected against tampering but not encrypted, e.g. a packet header.
Initialization Vector / "number used once": a per-message value that makes encrypting the same data twice give different output.
AES New Instructions: CPU instructions (Intel 2010, AMD and ARM equivalents) that run AES in hardware.
"Packed Carry-Less Multiplication Quadword": the CPU instruction that makes GCM's GHASH fast.
Add-Rotate-XOR: the only three operations ChaCha20 uses, which is why it runs in constant time in software.
Public-key cryptography
Rivest–Shamir–Adleman, the inventors' initials (1977). Security rests on how hard it is to factor a huge number.
Elliptic Curve Cryptography. Security rests on the elliptic-curve discrete logarithm problem (ECDLP).
Diffie–Hellman key exchange / its Ephemeral form (a fresh key pair per session).
Elliptic Curve Diffie–Hellman / its Ephemeral form. ECDHE is what modern TLS uses.
Digital Signature Algorithm / its Elliptic Curve version. Both need a perfect random number per signature.
Edwards-curve Digital Signature Algorithm, and its most common instance on the Ed25519 curve. Deterministic: no per-signature randomness to get wrong.
The Diffie–Hellman function on Curve25519 (RFC 7748).
Three names for the same NIST curve: NIST's name, the SEC (Standards for Efficient Cryptography) name, and the ANSI X9.62 name OpenSSL uses.
Optimal Asymmetric Encryption Padding: the safe way to encrypt with RSA.
Probabilistic Signature Scheme: the safe way to sign with RSA.
Public-Key Cryptography Standards, a numbered series started by RSA Labs. #1 = RSA, #7 = signed/enveloped data, #8 = private keys, #10 = CSRs, #12 = key+cert bundles.
Key Encapsulation Mechanism: "wrap a random secret for this public key", the post-quantum replacement for DH-style key exchange.
Module-Lattice KEM, Module-Lattice Digital Signature Algorithm, Stateless Hash-based DSA: the 2024 post-quantum standards (FIPS 203/204/205).
Hashing, MACs and key derivation
Message Digest 5 (1991). Broken: collisions in seconds.
Secure Hash Algorithm generations. SHA-1 broken; SHA-2 (SHA-256, SHA-384, SHA-512) is the workhorse; SHA-3 is the different-design backup.
Message Authentication Code: a short tag made with a secret key that proves a message is unmodified and came from a key holder.
Hash-based MAC: the standard way to build a MAC from a hash (RFC 2104).
Key Derivation Function: turns one secret into one or more keys of the right shape.
HMAC-based Extract-and-Expand KDF (RFC 5869), used by TLS 1.3, Signal and WireGuard.
Password-Based Key Derivation Function 2: repeated HMAC to make password guessing slow.
Pseudo-Random Function: TLS 1.2's name for its HMAC-based key derivation.
Cryptographically Secure Pseudo-Random Number Generator, e.g. /dev/urandom, os.urandom. Ordinary rand() is not one.
TLS and PKI
Transport Layer Security / its predecessor Secure Sockets Layer. Every SSL version is broken; "SSL certificate" is just habit.
Public Key Infrastructure: CAs, certificates, revocation, and the rules that bind them.
Certificate Authority / the CA/Browser Forum, where CAs and browser makers vote on the rules for public certificates.
The standard format for certificates.
Abstract Syntax Notation One (how a certificate's structure is described), Distinguished Encoding Rules (its binary encoding), Privacy-Enhanced Mail (the base64 text wrapper, a name left over from a 1990s email standard).
Certificate Signing Request (PKCS#10): what you send a CA.
Subject Alternative Name (the list of names a certificate is valid for) / Common Name (the old, ignored name field).
Extended Key Usage (what the cert may be used for) / Authority and Subject Key Identifiers (help chain building).
Authority Information Access: a URL in a certificate pointing at its issuer's certificate.
Object Identifier: a dotted number naming something globally, e.g. 2.23.140.1.2.1 = "Domain Validated".
Certificate Revocation List / Online Certificate Status Protocol: two ways of saying "this certificate is revoked".
Certificate Transparency / Signed Certificate Timestamp (a log's receipt) / Signed Tree Head (a log's signed summary).
Domain / Organisation / Extended Validation: how much a CA checked before issuing.
Hardware Security Module: a tamper-resistant device that holds keys and never lets them out.
Automatic Certificate Management Environment (RFC 8555): the protocol Let's Encrypt uses for automated certificates.
Server Name Indication (which site you want) / Application-Layer Protocol Negotiation (HTTP/2 or 1.1?) / Encrypted Client Hello (hides SNI).
Pre-Shared Key (used for resumption) / zero round-trip data sent with the first message.
HTTP Strict Transport Security / Certification Authority Authorization (a DNS record listing allowed CAs).
Forward Secrecy / "Perfect" Forward Secrecy: stealing the long-term key later can't decrypt past sessions.
Man-in-the-middle: an attacker relaying (and possibly altering) traffic between two parties.
A UDP-based transport with TLS 1.3 built in (used by HTTP/3) / Datagram TLS, TLS adapted for UDP.
The Big Picture: Four Primitives
A primitive is a basic building block with one job. Every protocol (TLS, SSH, Signal, disk encryption) is built by combining these four:
| Primitive | Job, in plain words | Examples | Key property |
|---|---|---|---|
| Symmetric encryption | Keep data secret between parties who share a key | AES-GCM, ChaCha20-Poly1305 | Fast; the same key encrypts and decrypts |
| Asymmetric (public-key) cryptography | Agree a key with a stranger; prove who signed something | RSA, ECDH, ECDSA, Ed25519 | Slow; a public/private key pair |
| Hashing | Make a fixed-size fingerprint of any data | SHA-256, SHA-3, BLAKE3 | One-way; the same input always gives the same output |
| MAC (Message Authentication Code) | Prove data wasn't changed, using a shared key | HMAC-SHA256, Poly1305 | Needs a shared secret key |
Rule of thumbasymmetric cryptography is used to agree a shared secret and prove identity, then symmetric cryptography takes over for the bulk data. This is TLS in a nutshell.
AES (Advanced Encryption Standard)
What is this?AES is a block cipher: a function that takes exactly 16 bytes (128 bits) of plaintext and a key, and outputs 16 scrambled bytes. With the key you can reverse it; without the key the output looks random. Keys are 128, 192 or 256 bits long.
Why it mattersAES is everywhere: TLS, disk encryption (FileVault, BitLocker, LUKS), VPNs, Wi-Fi (WPA2/WPA3), SSH, and cloud key services. NIST chose it in 2001 after an open, five-year public competition; the winning design was called Rijndael, by Joan Daemen and Vincent Rijmen (FIPS 197). Modern CPUs have dedicated AES instructions (AES-NI), so it runs at gigabytes per second. Against a future quantum computer, Grover's algorithm (see the quantum section) would halve its effective strength, so AES-256 keeps a comfortable 128-bit margin.
How it worksAES arranges the 16 bytes as a 4×4 grid and runs it through repeated rounds (10 rounds for a 128-bit key, 12 for 192, 14 for 256). Each round applies four steps:
-
SubBytestlsconfusion
- Every byte is swapped for another through a fixed lookup table (the S-box). Breaks any simple mathematical relationship.
-
ShiftRowstlsdiffusion across columns
- Row 1 shifts left by 0, row 2 by 1, row 3 by 2, row 4 by 3 places.
-
MixColumnstlsdiffusion within a column
- Each column is mixed so every output byte depends on all four input bytes. (Skipped in the last round.)
-
AddRoundKeydefendthe secret goes in
- XOR the grid with a round key derived from the main key.
After a few rounds, flipping one input bit changes about half of the output bits. That "avalanche" is what makes the output useless without the key.
Modes of operation: how to encrypt more than 16 bytes
AES alone only handles one 16-byte block. A mode of operation is the recipe for using it on a whole message. The choice of mode matters as much as the cipher itself:
| Mode | Full name | Integrity built in? | Needs | Use case |
|---|---|---|---|---|
| ECB | Electronic Codebook | No | Nothing | Never. Identical blocks give identical ciphertext, so patterns show through |
| CBC | Cipher Block Chaining | No | Random, unpredictable IV | Legacy TLS, old file formats; needs a separate MAC |
| CTR | Counter | No | Unique nonce | Fast streaming encryption; the core of GCM |
| GCM | Galois/Counter Mode | Yes (16-byte tag) | Unique 12-byte nonce | Default choice: TLS 1.3, SSH, IPsec, cloud KMS |
| CCM | Counter with CBC-MAC | Yes | Unique nonce | Wi-Fi (WPA2 CCMP), Bluetooth LE, IoT |
| GCM-SIV / SIV | Synthetic IV | Yes | Nonce, but survives reuse | Key wrapping, when nonce uniqueness can't be guaranteed |
| XTS | XEX Tweaked-codebook with ciphertext Stealing | No | Sector number as "tweak" | Full-disk encryption only |
How the three building-block modes chain blocks together:
ECB — each block encrypted alone (the flaw: same input block → same output block)
  P1 ──[AES k]──▶ C1      P2 ──[AES k]──▶ C2      P3 ──[AES k]──▶ C3

CBC — each plaintext block is XORed with the previous ciphertext before encrypting
  IV ─┐            C1 ─┐            C2 ─┐
  P1 ─⊕─[AES k]──▶ C1   P2 ─⊕─[AES k]──▶ C2   P3 ─⊕─[AES k]──▶ C3

CTR — AES encrypts a counter to make a keystream; the keystream is XORed with the data
  nonce‖1 ─[AES k]─▶ K1    nonce‖2 ─[AES k]─▶ K2    nonce‖3 ─[AES k]─▶ K3
            P1 ⊕ K1 = C1             P2 ⊕ K2 = C2             P3 ⊕ K3 = C3
  ← reuse the nonce and K1, K2, K3 repeat: C ⊕ C' = P ⊕ P', and the plaintext leaks
The famous illustration of ECB: encrypt a bitmap picture of the Linux penguin (Tux) in ECB mode, and the penguin's outline is still clearly visible in the "encrypted" image, because every identical patch of colour encrypts to an identical patch of noise.
AES-GCM in detailGCM is CTR-mode encryption plus an authentication tag computed by GHASH, a fast polynomial hash over the ciphertext and any AAD (additional authenticated data). The output is ciphertext + 16-byte tag.
- Decryption must check the tag before releasing any plaintext. Code that decrypts first and checks later turns into an oracle attackers can query.
- Critical weakness: nonce reuse is catastrophic. Two messages under the same key and nonce leak the XOR of their plaintexts and let an attacker recover the GHASH key and forge tags for any message.
- The nonce is 96 bits. Random nonces are fine for up to about 2³² messages per key (NIST's limit); beyond that, random collisions become a real risk (the "birthday bound").
- Named in TLS as
ECDHE-RSA-AES256-GCM-SHA384(TLS 1.2) orTLS_AES_256_GCM_SHA384(TLS 1.3).
In practice
from cryptography.hazmat.primitives.ciphers.aead import AESGCM
import os

key = os.urandom(32)        # 256-bit key from the OS CSPRNG
nonce = os.urandom(12)      # 96-bit nonce — never reuse with the same key!
data = b"secret message"
aad = b"authenticated but not encrypted"     # e.g. a record header

aesgcm = AESGCM(key)
ciphertext = aesgcm.encrypt(nonce, data, aad)   # ciphertext + 16-byte tag
plaintext = aesgcm.decrypt(nonce, ciphertext, aad) # raises InvalidTag if anything was altered📰Real incident — "Nonce-Disrespecting Adversaries" (2016). Researchers scanned the internet and found 184 HTTPS servers that repeated AES-GCM nonces, including sites of major organisations; about 70,000 more used random nonces (risky at volume). On the repeating servers they could forge content into the encrypted pages. Lesson: GCM is only as safe as the nonce handling in the TLS library underneath.
Advantages and disadvantagesGCM gives encryption and integrity in one pass, is hardware-accelerated (AES-NI + PCLMULQDQ) and is the most studied AEAD. But nonce misuse is fatal (unlike AES-GCM-SIV), and software implementations without hardware support risk timing side channels (the S-box table lookups depend on secret data and leak through the CPU cache).
ChaCha20-Poly1305
What is this?A second AEAD, built from two parts designed by Daniel J. Bernstein: ChaCha20, a stream cipher (it generates a keystream to XOR with the data, like AES-CTR), and Poly1305, a one-time MAC that produces the 16-byte tag. Standardised in RFC 8439.
Why it mattersIt's the alternative for devices without AES hardware (older and cheaper phones, IoT). It uses only ARX operations (32-bit Add, Rotate, XOR), which take the same time whatever the data, so it's naturally resistant to timing side channels even in pure software. Used in TLS 1.3 (TLS_CHACHA20_POLY1305_SHA256), WireGuard, Signal, and OpenSSH (chacha20-poly1305@openssh.com).
How it works
ChaCha20 state: 16 words of 32 bits (a 4×4 grid, 512 bits)
  ┌──────────────┬──────────────┬──────────────┬──────────────┐
  │ "expa"       │ "nd 3"       │ "2-by"       │ "te k"       │  ← fixed constants
  │ key[0]       │ key[1]       │ key[2]       │ key[3]       │  ← 256-bit key
  │ key[4]       │ key[5]       │ key[6]       │ key[7]       │
  │ counter      │ nonce[0]     │ nonce[1]     │ nonce[2]     │  ← block counter + 96-bit nonce
  └──────────────┴──────────────┴──────────────┴──────────────┘
  20 rounds of "quarter-rounds" (a += b; d ^= a; d <<<= 16; …) scramble the grid.
  Output = scrambled grid + original grid → 64 bytes of keystream. Counter += 1 for the next 64 bytes.

Poly1305: the first keystream block becomes a one-time key (r, s). The ciphertext is treated as
the coefficients of a polynomial, evaluated at r modulo the prime 2^130 − 5, then s is added → 16-byte tag.
| AES-GCM | ChaCha20-Poly1305 | |
|---|---|---|
| Speed with AES hardware | Faster | Slower |
| Speed without AES hardware | Slower | Faster, often several times on low-end phones |
| Timing side channels in software | Risky (table lookups) | Safe (ARX only) |
| Nonce reuse | Catastrophic | Also catastrophic for confidentiality and the tag |
| Nonce size | 96 bits | 96 bits (XChaCha20 variant: 192 bits, safe to pick at random) |
| Key size | 128 or 256 bits | 256 bits |
🎯On the job. A TLS server should offer both and let the client choose (Mozilla's "intermediate" profile): phones without AES hardware pick ChaCha20, laptops pick AES-GCM. If you need random nonces for a huge number of messages under one key, use XChaCha20-Poly1305, whose 192-bit nonce makes random collisions practically impossible.
RSA
What is this?RSA, named after Rivest, Shamir and Adleman (1977), was the first practical public-key system. It can encrypt (anyone with the public key can lock data only the private key opens) and sign (only the private key can produce a signature anyone can verify). Key sizes are 2048, 3072 or 4096 bits.
Why it mattersIt still signs most TLS certificates, S/MIME email, PGP keys, and JWTs marked RS256/PS256. TLS 1.2 also used it to transport the session key, which is why recorded TLS 1.2 RSA sessions can be decrypted later if the key leaks.
How it worksMultiplying two big primes is easy; splitting the product back into them (factoring) is infeasible at 2048+ bits. A toy example with tiny numbers shows every step:
Key generation
  p = 61, q = 53                   two secret primes
  n = p × q = 3233                 the public modulus (2048+ bits in real life)
  φ(n) = (p−1)(q−1) = 3120         Euler's totient; computable only if you know p and q
  e = 17                           public exponent (real keys almost always use 65537)
  d = e⁻¹ mod φ(n) = 2753          private exponent: 17 × 2753 = 46801 = 15 × 3120 + 1

Public key: (n=3233, e=17)         Private key: d=2753 (plus p, q)

Encrypt m = 65:   c = 65^17 mod 3233 = 2790
Decrypt c:        m = 2790^2753 mod 3233 = 65   ✓
Sign:   sig = hash(m)^d mod n          Verify:  hash(m) == sig^e mod n
Anyone who can factor 3233 into 61 × 53 can compute d. For a 2048-bit n nobody can, as far as is publicly known.
Key strengthBigger RSA keys don't scale well: security grows slowly with size, while ECC grows linearly. Equivalent strengths (NIST SP 800-57):
| Security level | RSA modulus | ECC key | Status |
|---|---|---|---|
| 80-bit | 1024 | 160 | Broken / disallowed |
| 112-bit | 2048 | 224 | Minimum today; NIST plans to deprecate it after 2030 |
| 128-bit | 3072 | 256 | Recommended |
| 192-bit | 7680 | 384 | High security |
| 256-bit | 15360 | 512–521 | Top level |
(RSA-4096, a popular choice, lands at roughly 140–150 bits: stronger than 3072, far from 192.)
Padding: why "textbook RSA" is unsafeThe raw formula above is deterministic (the same message always gives the same ciphertext, so guesses can be checked) and malleable (multiplying a ciphertext changes the plaintext predictably). Real RSA always adds structured randomness, called padding, first:
| Scheme | Full name | Use | Status |
|---|---|---|---|
| PKCS#1 v1.5 | Public-Key Cryptography Standard #1, version 1.5 | Encryption and signatures | Encryption broken by Bleichenbacher's padding-oracle attack (1998) and its revival ROBOT (2017); v1.5 signatures are still acceptable and widely used |
| OAEP | Optimal Asymmetric Encryption Padding | Encryption | Recommended; randomised, with a security proof |
| PSS | Probabilistic Signature Scheme | Signatures | Recommended; required for RSA signatures in the TLS 1.3 handshake |
A padding oracle is any server behaviour (a different error message, a different response time) that tells an attacker whether a modified ciphertext had valid padding. Bleichenbacher showed that about a million such questions are enough to decrypt a captured RSA ciphertext without the key.
Advantageswell understood, simple to verify signatures, huge ecosystem. Disadvantages: large keys and signatures (a 3072-bit signature is 384 bytes vs 64 for Ed25519), slow key generation and signing, needs blinding to resist timing attacks, padding pitfalls, and it's broken outright by a large quantum computer (Shor's algorithm).
Elliptic Curve Cryptography (ECC)
Last verified2026-10
What is this?ECC is public-key cryptography built on the points of a special kind of curve. It does the same jobs as RSA and classic Diffie–Hellman (key exchange and signatures), but with much smaller keys: a 256-bit ECC key is about as strong as a 3072-bit RSA key. Neal Koblitz and Victor Miller proposed it independently in 1985.
Why it mattersAlmost every modern handshake uses it: TLS (ECDHE key exchange, ECDSA certificates), SSH (ssh-ed25519 keys), Signal and WhatsApp (X25519), WireGuard, Apple and Android device keys, passkeys/WebAuthn (P-256), JWTs (ES256), and Bitcoin and Ethereum (secp256k1). Interviewers ask about curve names, why Ed25519 is safer than ECDSA, and what went wrong at Sony and in Windows' CurveBall bug.
What an elliptic curve is
An elliptic curve is the set of points (x, y) that satisfy an equation of the form
y² = x³ + a·x + b (the "short Weierstrass" form; a and b are fixed numbers that define the curve)Despite the name, it has nothing to do with ellipses. Over ordinary real numbers it looks like a smooth line, symmetric above and below the x-axis. The magic is that you can "add" two points on the curve and get a third point on the curve:
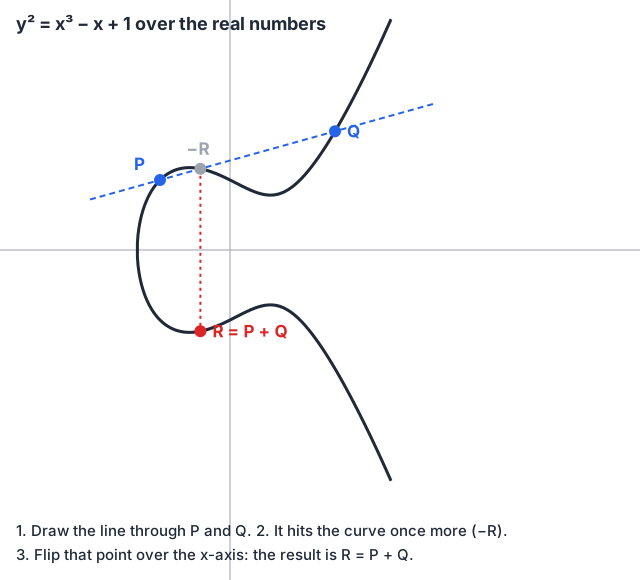
-
Point addition P + Qtlstwo different points
- Draw the straight line through P and Q. It always hits the curve at exactly one more point.
- Reflect that third point over the x-axis. That reflection is defined as P + Q.
-
Point doubling P + Ptlsthe same point twice
- Use the tangent line at P instead, then reflect the second intersection.
-
Scalar multiplication k·Pdefendthe operation all ECC is built on
- k·P means P + P + … + P (k times). Computed fast by "double-and-add": 2P, 4P, 8P … and adding the ones you need.
- Even a 256-bit k takes only about 256 doublings and ~128 additions.
-
The hard problem (ECDLP)attackthe reverse direction
- Given P and Q = k·P, find k. No known classical method does much better than about √n steps, where n is the number of points.
A private key is a random number k. The public key is the point k·G, where G is a fixed starting point (the generator or base point) that is part of the curve's definition. Going from k to k·G takes microseconds. Going back from k·G to k is the elliptic curve discrete logarithm problem (ECDLP), and for a 256-bit curve it would take around 2¹²⁸ operations. That square root is why a 256-bit curve gives "128-bit security".
From smooth curves to scattered dots: the finite field
Computers can't use real numbers, because rounding errors would break the maths. Real ECC works with whole numbers modulo a prime p (a finite field): every addition and multiplication wraps around at p. The same equation then gives a finite set of points that look randomly scattered, but the addition rules still work exactly.
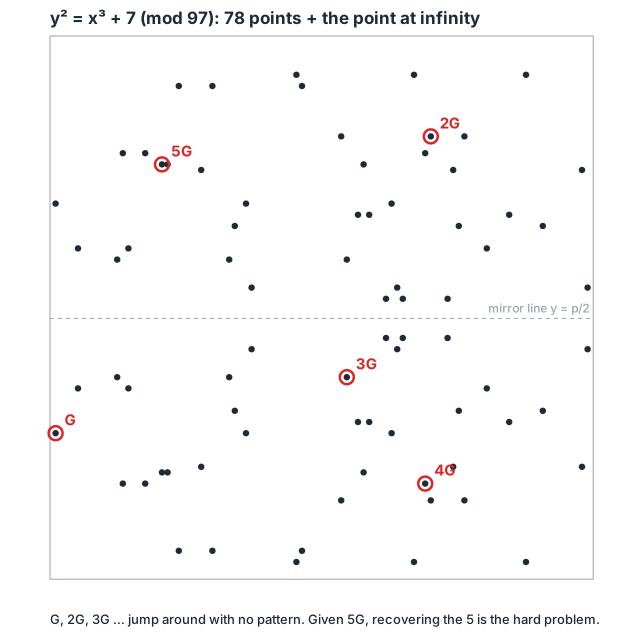
That graph is the equation used by Bitcoin's curve (secp256k1), but with the tiny prime 97 instead of a 256-bit one. Notice two things:
- The points are mirrored around the middle line, because if (x, y) is on the curve, so is (x, p − y), the finite-field version of "reflect over the x-axis".
- G, 2G, 3G, 4G, 5G jump around with no visible pattern. With 79 elements you could just try every k. With about 2²⁵⁶ points, you can't.
The modulus all arithmetic wraps around. Many curves are named after it: Curve25519 uses p = 2²⁵⁵ − 19.
The agreed starting point. Every public key is some multiple of it.
How many times you add G to itself before getting back to the start (the "point at infinity", which acts as zero). Private keys are numbers from 1 to n−1.
Total number of points ÷ n. P-256 and secp256k1 have h = 1; Curve25519 has h = 8, which libraries handle by "clamping" private keys.
The identity element: P + (−P) gives it, like x + (−x) = 0. It isn't on the drawing, but the maths needs it.
A curve over a field of size p has about p + 1 points (within ±2√p). So a 256-bit prime gives about 2²⁵⁶ points.
How many curves exist?
Mathematically, unlimited: every prime p and every pair (a, b) with 4a³ + 27b² ≠ 0 defines a curve, so for a 256-bit prime there are around 2²⁵⁷ distinct curves. But choosing a good curve is hard. The number of points must have a large prime factor, the curve must avoid several known weak families, and implementations need formulas that are fast and constant-time. So the world uses a small set of named curves with published, vetted parameters:
- OpenSSL 3.6 knows 82 named curves (
openssl ecparam -list_curves), mostly legacy or niche. - Standards bodies recommend about 10: NIST SP 800-186 (2023) lists the P-curves, Curve25519/Curve448 and their Edwards forms, plus binary curves kept only for legacy systems.
- A browser in 2026 offers 3–4 in a TLS ClientHello: X25519MLKEM768 (hybrid post-quantum), X25519, P-256, P-384.
The curves you'll actually meet
| Curve | Also called | Equation form | Security | Where you see it |
|---|---|---|---|---|
| P-256 | secp256r1, prime256v1 | Weierstrass, a = −3 | 128-bit | TLS certificates and key exchange, passkeys/WebAuthn, smart cards, ES256 JWTs, AWS KMS |
| P-384 | secp384r1 | Weierstrass, a = −3 | 192-bit | Government and compliance (US CNSA suite), CA root keys |
| P-521 | secp521r1 | Weierstrass | ~256-bit | Rare; the 521 is not a typo (the prime is 2⁵²¹ − 1) |
| secp256k1 | "Koblitz curve" | Weierstrass, a = 0, b = 7 | 128-bit | Bitcoin, Ethereum and most cryptocurrencies |
| Curve25519 | X25519 (the DH function) | Montgomery: y² = x³ + 486662x² + x | 128-bit | TLS key exchange (most popular group), SSH, Signal, WireGuard |
| Ed25519 | edwards25519 | Twisted Edwards: −x² + y² = 1 − (121665/121666)x²y² | 128-bit | SSH keys, signatures in Signal, Tor, age, package signing, TLS 1.3 (rarely in certificates) |
| Curve448 / Ed448 | X448, "Goldilocks" | Montgomery / Edwards | 224-bit | High-security alternative to 25519; uncommon |
| brainpoolP256r1 (and 384, 512) | Brainpool | Weierstrass, verifiably random | 128-bit | European government and banking, German eID (BSI) |
| SM2 | — | Weierstrass | 128-bit | Chinese national standard |
How to read the names:
sec  p  256  r  1
 │   │   │   │  └─ 1   = first curve of this type and size
 │   │   │   └──── r   = parameters chosen (verifiably) at random; k = Koblitz, special efficient parameters
 │   │   └──────── 256 = size of the field in bits
 │   └──────────── p   = curve over a prime field (t = binary field, as in sect233k1)
 └──────────────── sec = SEC 2, "Standards for Efficient Cryptography" (Certicom, 2000)

Curve25519  →  named after its prime, 2^255 − 19
Ed25519     →  Edwards-curve signatures over that same field (the two curves are mathematically equivalent shapes)
Three equation families, and why they matter. All three describe the same kind of mathematical object, written differently for speed and safety:
The textbook form. Its addition formulas have special cases (adding a point to itself, to its negative, to infinity) that implementations must handle in constant time; mistakes have leaked keys.
Allows the "Montgomery ladder": computing k·P with the same sequence of operations for every k, so timing reveals nothing. Only the x-coordinate is used, which keeps X25519 tiny and simple.
Has one "complete" addition formula with no special cases at all, so the same code handles every input. That's why EdDSA is fast and hard to implement wrongly.
The trust question: NIST curves vs "nothing up my sleeve"
P-256 and friends were published by NIST in 1999–2000 with constants generated by hashing a seed that the NSA supplied without explaining where it came from. Nobody has found a weakness in P-256. But after the 2013 Snowden documents confirmed that the NSA had backdoored Dual_EC_DRBG, a NIST random-number generator that used points on P-256 (the backdoor was in the generator's choice of points, not the curve itself), trust in unexplained constants collapsed. Curve25519 was designed with every constant justified ("nothing up my sleeve"): the prime is the closest to 2²⁵⁵, and 486662 is the smallest value meeting the stated security criteria. That, plus speed and simplicity, is why X25519 became the default key exchange on the web. Brainpool curves use verifiably random parameters for the same reason.
ECDH, ECDSA and EdDSA
ECDH (Elliptic Curve Diffie–Hellman) agrees a shared secret:
Alice: private a, public A = a·G   ──── A ────▶
Bob:   private b, public B = b·G   ◀─── B ─────
Alice computes a·B = a·(b·G)      Bob computes b·A = b·(a·G)      Both = ab·G  (the shared secret)
An eavesdropper sees A and B but would need a or b, which is the ECDLP.
ECDSA (Elliptic Curve Digital Signature Algorithm) signs with the private key, but it needs a fresh, secret, uniformly random number k for every signature:
- Reusing
kwith the same key, even once, lets anyone solve two equations for the private key. - Even a slightly biased
k(a few predictable bits) leaks the key once an attacker collects enough signatures (lattice attacks). - The modern fix is deterministic
k(RFC 6979: derive it from the key and message hash).
EdDSA (Ed25519) builds deterministic nonces in from the start (k = hash of a secret key half and the message), uses complete Edwards formulas, and has a single fixed curve and hash. Nothing to choose, nothing random to get wrong.
📰Real incident — Sony PlayStation 3 (2010). Sony signed PS3 software with ECDSA but used the same
kfor every signature. The fail0verflow group took two signatures, solved for Sony's private signing key, and from then on anyone could sign their own software as Sony. Similar mistakes (weak random numbers in Android's Java SecureRandom in 2013) let thieves compute private keys for Bitcoin wallets and empty them.
📰Real incident — CurveBall (CVE-2020-0601). Windows' certificate validation (crypt32.dll) accepted certificates that described their own curve parameters, including their own generator point G, and only compared the public key with the trusted root's. An attacker could choose a G for which they knew the private key matching a real root CA's public key, and forge certificates for any website or code signer. Reported to Microsoft by the NSA in January 2020. Lesson: only accept named curves; never let input define the curve.
🎯On the job. For new systems: X25519 for key exchange, Ed25519 for signatures, P-256 where compliance (FIPS) or hardware (smart cards, HSMs, passkeys, cloud KMS) requires NIST curves. In review, flag ECDSA code that generates
kitself, libraries that don't check received points are on the curve (invalid-curve attacks let an attacker pull out a private key bit by bit), and any certificate or protocol that allows explicit curve parameters instead of a named curve.
Advantagessmall keys (32 bytes vs 256+ for RSA), small signatures (64 bytes), fast. Disadvantages: more ways to implement it wrongly (nonces, point validation, side channels), and broken by a large quantum computer just like RSA (Shor's algorithm also solves the ECDLP).
Diffie-Hellman Key Exchange (DH / ECDH)
What is this?A way for two parties to create the same secret number while an eavesdropper watches everything they send. Whitfield Diffie and Martin Hellman published it in 1976; it's the idea underneath every modern key exchange.
Why it mattersIt's what gives forward secrecy, and the classic "paint mixing" picture is a favourite interview explanation: both sides start with a public colour, each mixes in a secret colour and swaps the result, then each adds its own secret again. Both end with the same final colour, and nobody can "unmix" paint to find the secrets.
How it worksThe finite-field version (FFDH), with small numbers:
Public, agreed in advance:  prime p = 23, generator g = 5
Alice picks secret a = 4     →  A = 5⁴ mod 23 = 4     → sends 4
Bob picks secret   b = 3     →  B = 5³ mod 23 = 10    → sends 10
Alice: S = 10⁴ mod 23 = 18
Bob:   S = 4³  mod 23 = 18      ← same secret; the wire only ever carried 23, 5, 4 and 10
Recovering a from A = gᵃ mod p is the discrete logarithm problem. Real deployments use 2048-bit or larger primes (the named "ffdhe" groups of RFC 7919), or the elliptic-curve version, ECDH, which gets the same security from 256-bit numbers.
Forward secrecy comes from ephemeral keys (the "E" in DHE/ECDHE): a fresh key pair for each session, deleted afterwards. If the server's long-term key leaks later, past sessions can't be decrypted, because the secrets that protected them no longer exist anywhere.
| Protocol | Key exchange | Forward secrecy? |
|---|---|---|
| TLS 1.2 with RSA key transport | Client encrypts the secret to the server's RSA key | No |
| TLS 1.2 with ECDHE | Ephemeral ECDH | Yes |
| TLS 1.3 | (EC)DHE always, or hybrid post-quantum | Yes (always) |
Security angleDH alone doesn't say who you agreed a secret with. A man-in-the-middle can run one exchange with each side. TLS fixes that by having the server sign its DH value with its certificate key. Weak groups are the other trap: Logjam (2015) downgraded connections to 512-bit "export" DH, and showed that a well-funded attacker could precompute against the few 1024-bit primes most servers shared.
Hashing Algorithms
What is this?A cryptographic hash function turns any input (a password, a file, a certificate) into a fixed-size fingerprint, the digest. It must be fast to compute and impossible to run backwards.
Why it mattersHashes sit inside almost everything: digital signatures sign a hash, certificates are identified by hash, Git and backups detect changes by hash, software downloads are checked by hash, and password storage uses (slow) hashes.
How it worksA secure hash has three properties, each defeated by a different attack:
Given a digest, you can't find any input that produces it. ("Reverse the fingerprint.")
Given one input, you can't find a different input with the same digest. ("Forge a document matching this one.")
You can't find any two inputs with the same digest. The weakest link: because of the birthday paradox, it only takes about 2^(n/2) tries for an n-bit hash, so a 256-bit hash gives 128-bit collision security.
There are two main internal designs:
Merkle–Damgård (MD5, SHA-1, SHA-2): chop the message into blocks and feed them through a compression function in a chain.
  IV ─▶[f]─▶[f]─▶[f]─▶ digest = the final internal state
        ▲    ▲    ▲
       M1   M2   M3
  Side effect: knowing H(secret ‖ msg) lets you compute H(secret ‖ msg ‖ padding ‖ more) → "length extension"

Sponge (SHA-3 / Keccak): "absorb" the message into a large state, then "squeeze" out as many output bits as needed.
The output reveals only part of the state, so no length extension, and output length is flexible (SHAKE128/256).| Algorithm | Full name / origin | Output | Status |
|---|---|---|---|
| MD5 | Message Digest 5 (Ron Rivest, 1991) | 128 bits | Broken: collisions in seconds since 2004. Only for non-security checksums |
| SHA-1 | Secure Hash Algorithm 1 (NSA/NIST, 1995) | 160 bits | Broken: first collision "SHAttered" (2017), chosen-prefix collisions (2020). Banned for certificates |
| SHA-256 / SHA-224 | SHA-2 family (NSA/NIST, 2001) | 256 / 224 bits | Secure, the default everywhere |
| SHA-512 / SHA-384 | SHA-2 family, 64-bit design | 512 / 384 bits | Secure; often faster than SHA-256 on 64-bit CPUs. SHA-384 is truncated, so no length extension |
| SHA-3 (SHA3-256 …) / SHAKE | Keccak sponge, won NIST competition 2012; FIPS 202 (2015) | 224–512 bits, any length for SHAKE | Secure; a different design kept as backup if SHA-2 ever falls |
| BLAKE2 (b/s) | Successor of SHA-3 finalist BLAKE (2012) | up to 512 / 256 bits | Secure; faster than SHA-2 in software. Used in WireGuard, Argon2 |
| BLAKE3 | 2020 | 256 bits (extendable) | Secure; tree structure, parallel across cores, extremely fast |
Password hashes are a different toolNormal hashes are designed to be fast, which is exactly wrong for passwords: a GPU computes billions of SHA-256 hashes per second. Password hashing functions are deliberately slow and use a unique random salt per user so identical passwords get different hashes:
| Function | Full name / origin | What makes it slow | Status |
|---|---|---|---|
| Argon2id | Winner of the Password Hashing Competition (2015), RFC 9106 | Time and memory (memory-hard) | Recommended for new systems |
| scrypt | Colin Percival, 2009 | Memory-hard | Good; also used to derive disk and wallet keys |
| bcrypt | Provos and Mazières, 1999, based on the Blowfish cipher | Expensive key setup, cost factor doubles work | Still acceptable; truncates passwords at 72 bytes |
| PBKDF2 | Password-Based Key Derivation Function 2 (RFC 8018) | Iterated HMAC | Acceptable only with very high iteration counts; required in FIPS environments |
Where each is used
- SHA-256: certificate and code signatures, HMAC-SHA256, Bitcoin proof-of-work, package checksums, Docker image digests (
sha256:…) - SHA-384: TLS 1.3 suites with AES-256 (
TLS_AES_256_GCM_SHA384), high-assurance certificates - SHA-1: still inside Git object IDs (with collision detection; SHA-256 repositories are optional), legacy HMAC-SHA1 (HMAC is still safe with SHA-1)
- SHA-3: government and long-term systems wanting a non-SHA-2 design; not used by TLS cipher suites
- BLAKE2s/BLAKE3: WireGuard, fast file checksums and deduplication
- Argon2id / bcrypt / scrypt: user password storage
📰Real incident — Flame malware (2012). The Flame espionage malware was signed with a forged Microsoft code-signing certificate. Its authors used a new MD5 chosen-prefix collision against a Microsoft licensing CA that still signed with MD5, so Windows Update clients accepted the malware as genuine. Lesson: a "theoretically broken" hash becomes a practical forgery tool for a well-funded attacker; retire it from signatures as soon as collisions appear.
TLS in Depth
Last verified2026-10
What is this?TLS (Transport Layer Security, the successor to SSL, Secure Sockets Layer) is the protocol that puts the "S" in HTTPS, SMTPS, IMAPS and LDAPS (the protected versions of web, mail-sending, mail-reading and directory traffic) and most service-to-service traffic. It sits between TCP (or QUIC, the UDP-based transport behind HTTP/3) and the application, and turns an untrusted network path into a private, tamper-evident channel to a server whose identity has been checked. The sections below go from first principles to byte-level detail: the cryptography it uses, certificates and PKI, cipher suites, the record layer, both handshakes, the defenses built around TLS, the attacks that shaped it, and the TLS 1.3 key schedule.
Why it mattersAlmost every security question about the web eventually lands on TLS: "how do you know you're talking to the real bank?", "what does a MITM (man-in-the-middle) proxy actually do?", "why did we disable TLS 1.0?", "why can't the SOC (security operations centre) see inside this traffic anymore?". Interviewers use TLS to probe whether you understand cryptography as a system: which primitive does which job, and what fails when one is missing.
The primitives themselves (AES, ChaCha20, RSA, ECC, Diffie–Hellman, hashing, HMAC, HKDF) are covered earlier on this page. This part is about how TLS assembles them.
What TLS guarantees (and doesn't), who the players are, how versions evolved.
Which primitive does which job in the handshake and the record layer.
X.509 structure, extensions, private keys, CSRs, file formats.
Chains, constraints, DV/OV/EV, CRL, OCSP, CRLSets, CRLite, short-lived certs.
Key exchange, authentication, bulk encryption, hashing; forward secrecy; what to allow.
The record layer, TLS 1.2 handshake variants, resumption, mutual TLS, extensions.
HSTS, CAA, Certificate Transparency; BEAST to Raccoon and what each one taught.
What changed, why, the key schedule, PSK, 0-RTT, and the 1.3 extensions.
TLS Fundamentals: Goals, Players and Versions
What TLS protects
Only the two endpoints can read the data. Provided by symmetric encryption (AES-GCM, ChaCha20-Poly1305) with keys agreed during the handshake.
Any change to the data in transit is detected. Provided by a MAC (TLS 1.2 CBC suites) or an AEAD tag (GCM / Poly1305).
The client knows it's talking to the real server (and optionally vice versa). Provided by certificates + digital signatures.
A recorded record can't be re-injected later. Every record has an implicit sequence number mixed into the MAC/nonce, so a replayed or reordered record fails verification.
WarningTLS does not give non-repudiationBoth sides hold the same symmetric session keys, so either side could have produced any given record. A packet capture of a TLS session can't prove to a third party that the server sent a particular message. That needs an application-level signature (e.g. signed JWTs, S/MIME, document signing). Interviewers like this trap.
The players
Starts the connection, offers its capabilities, validates the server's certificate. Usually a browser, an SDK or a service.
Picks the parameters, proves its identity with a certificate and a signature made with its private key.
A third party both sides trust. It verifies the server controls the domain, then signs a certificate binding the domain name to the server's public key.
The list of CA roots a client trusts out of the box (Chrome Root Store, Mozilla NSS (Network Security Services, Firefox's crypto library), Apple, Microsoft). Root program policy is what actually governs CAs.
Public, append-only logs every publicly trusted certificate must be submitted to, so mis-issuance can be spotted.
Versions
| Version | Year | Spec | Wire value | Status |
|---|---|---|---|---|
| SSL 2.0 | 1995 | Netscape | 0x0002 | Prohibited (RFC 6176, 2011) — broken by design |
| SSL 3.0 | 1996 | RFC 6101 (historic) | 0x0300 | Deprecated (RFC 7568, 2015) after POODLE |
| TLS 1.0 | 1999 | RFC 2246 | 0x0301 | Deprecated (RFC 8996, 2021) — BEAST, weak PRF (the MD5+SHA-1 key-derivation function) |
| TLS 1.1 | 2006 | RFC 4346 | 0x0302 | Deprecated (RFC 8996, 2021) — no AEAD (authenticated encryption) suites, MD5+SHA-1 PRF |
| TLS 1.2 | 2008 | RFC 5246 | 0x0303 | Acceptable with AEAD + ECDHE suites only |
| TLS 1.3 | 2018 | RFC 8446 | 0x0304 | Preferred everywhere |
Memory hook"TLS 1.0 is SSL 3.1"The wire version for TLS 1.0 is
3,1(0x0301), TLS 1.2 is3,3, TLS 1.3 is3,4. The rename from SSL to TLS was mostly political (Netscape → IETF), not a redesign. That's why "SSL certificate" and "SSL offload" are still everyday terms, even though no one should be running SSL.
How TLS Uses Cryptography
TLS is a hybrid system. Asymmetric cryptography is slow but solves the "how do two strangers agree on a secret and know who they're talking to" problem. Symmetric cryptography is fast and protects the bulk data. Hashes glue everything together.
-
Key exchange — Diffie–Hellman (ECDHE)Handshake
Both sides send a public value, and each combines the other's with its own private value to reach the same shared secret. The secret itself never crosses the wire. (TLS 1.2 also allowed RSA key transport: the client encrypted a secret to the server's RSA key.)
-
Authentication — digital signaturesHandshake
The server signs handshake data with the private key matching its certificate (RSA-PSS, ECDSA or Ed25519). The CA's signature on the certificate binds that key to the domain name.
-
Key derivation — hash-based KDFHandshake
The raw shared secret is stretched into separate keys and IVs for each direction: the TLS 1.2 PRF (HMAC-SHA256/384) or TLS 1.3 HKDF.
-
Transcript integrity — hashingHandshake
A running hash of every handshake message is signed (CertificateVerify) and MACed (Finished), so tampering with any earlier message is caught.
-
Bulk protection — symmetric AEADRecords
Application data is encrypted and authenticated with AES-GCM or ChaCha20-Poly1305, using the derived keys and a per-record nonce.
| Primitive | TLS 1.2 uses it for | TLS 1.3 uses it for |
|---|---|---|
| RSA | Key transport or signatures | Signatures only (RSA-PSS for handshake signatures) |
| (EC)DHE | Optional key exchange | The only full-handshake key exchange (plus PSK) |
| ECDSA / EdDSA | Signatures (ECDSA) | Signatures (ECDSA, Ed25519, Ed448) |
| DSA | Rare, allowed | Removed |
| Hash | PRF, Finished, signatures | HKDF, transcript hash, signatures |
| Symmetric | AES-CBC+HMAC, AES-GCM, ChaCha20, (RC4, 3DES) | AEAD only: AES-GCM, ChaCha20-Poly1305, AES-CCM |
Memory hook"RSA wears two hats; TLS 1.3 took one away." RSA can encrypt a secret (key transport) or sign (authentication). Key transport means whoever later steals the server's private key can decrypt every recorded session, so TLS 1.3 kept only the signing hat. That single change is why TLS 1.3 always has forward secrecy.
X.509 Certificates, Keys and CSRs
What's in a certificate
A certificate is a signed statement from a CA: "the holder of this public key is entitled to use these names, from this date to that date". The structure is described in ASN.1 (Abstract Syntax Notation One), encoded with DER (Distinguished Encoding Rules, a strict binary format) and usually shipped as PEM (Privacy-Enhanced Mail: the DER bytes in base64 between -----BEGIN CERTIFICATE----- lines; the name is a leftover from a 1990s email standard).
- tbsCertificate
- "To Be Signed": version, serial, issuer, validity, subject, public key, extensions
- signatureAlgorithm
- Which algorithm the CA used, e.g. ecdsa-with-SHA384, sha256WithRSAEncryption
- signatureValue
- The CA's signature over the DER bytes of tbsCertificate
Certificate:
  Version: 3
  Serial Number: 04:a1:...              ← unique per CA; ≥ 64 random bits from a CSPRNG (CA/Browser Forum rule)
  Signature Algorithm: ecdsa-with-SHA384
  Issuer: C=US, O=Let's Encrypt, CN=E6  ← must byte-match the issuer cert's Subject
  Validity:
    Not Before: Jun  1 00:00:00 2026 GMT
    Not After : Aug 30 00:00:00 2026 GMT
  Subject: CN=example.com               ← informational only; browsers ignore CN for matching
  Subject Public Key Info:
    Public Key Algorithm: id-ecPublicKey (P-256)
    Public Key: 04:6b:... (65 bytes)
  X509v3 extensions:
    Subject Alternative Name: DNS:example.com, DNS:www.example.com
    Basic Constraints: critical, CA:FALSE
    Key Usage: critical, Digital Signature
    Extended Key Usage: TLS Web Server Authentication
    Authority Key Identifier: 93:27:...
    Subject Key Identifier: 1f:c2:...
    Authority Information Access: CA Issuers - URI:http://e6.i.lencr.org/
    Certificate Policies: 2.23.140.1.2.1    ← CA/B Forum "Domain Validated" policy OID
CT Precertificate SCTs: (2 SCTs from different log operators)Certificate extensions that matter
| Extension | What it says | Security relevance |
|---|---|---|
| Subject Alternative Name | DNS names / IPs the cert is valid for | The only field used for hostname matching |
| Basic Constraints | CA:TRUE/FALSE, optional pathLenConstraint | A leaf with CA:TRUE could mint certificates; old IE bugs ignored this |
| Key Usage | Low-level operations: digitalSignature, keyEncipherment, keyCertSign, cRLSign | Stops a leaf key being used to sign certificates |
| Extended Key Usage | Purpose: serverAuth, clientAuth, codeSigning, emailProtection | A code-signing cert must not authenticate a web server |
| Name Constraints | Permitted / excluded name subtrees for a CA | Lets an org get a CA restricted to *.corp.example |
| AKI / SKI | Key identifiers of issuer / subject | Helps path building pick the right issuer when names collide |
| Authority Information Access | URL of the issuer cert (and formerly OCSP) | Lets clients fetch missing intermediates ("AIA chasing") |
| CRL Distribution Points | Where to download the CRL | Revocation |
| Certificate Policies | OIDs for DV / OV / EV and CA policy | How a client knows the validation level |
| SCT list | Signed Certificate Timestamps from CT logs | Required by Chrome and Apple for public trust |
| TLS Feature (must-staple) | Server must staple an OCSP response | Hard-fail revocation (RFC 7633); rarely deployed |
Critical flagAn extension marked critical must be understood by the client, or the certificate must be rejected. Basic Constraints and Key Usage are normally critical; SAN is critical only when the Subject is empty.
What's in a private key
Modulus n, public exponent e (65537), private exponent d, primes p and q, plus CRT (Chinese Remainder Theorem) helpers dP, dQ, qInv that speed up signing ~4× by working modulo p and q separately. Knowing p or q is as good as knowing d.
A single random integer (the scalar) and the curve name, e.g. P-256. The public key is that scalar × the curve's base point.
A 32-byte seed, hashed to produce the signing scalar. No curve parameters to choose, no per-signature randomness to get wrong.
PKCS#1 (BEGIN RSA PRIVATE KEY, RSA only), PKCS#8 (BEGIN PRIVATE KEY, any algorithm), encrypted PKCS#8 (BEGIN ENCRYPTED PRIVATE KEY), SEC1 (BEGIN EC PRIVATE KEY, the EC-only format from the SEC 1 standard).
Matching a certificate to its private key. They match if they contain the same public key. Compare hashes of the public key, not of the files:
openssl x509 -in cert.pem -noout -pubkey | openssl sha256
openssl pkey -in key.pem -pubout          | openssl sha256
openssl req -in req.csr -noout -pubkey | openssl sha256 # the CSR should match tooWhat's in a CSR
A Certificate Signing Request (CSR, defined in PKCS#10) is what you send a CA: your subject, your public key, the extensions you'd like (usually SANs), all signed with your private key. That self-signature is proof of possession: you can't request a certificate for someone else's public key. The private key never leaves your machine.
# New P-256 key + CSR with SANs in one step
openssl req -new -newkey ec -pkeyopt ec_paramgen_curve:P-256 -nodes \
  -keyout example.key -out example.csr \
  -subj "/CN=example.com" -addext "subjectAltName=DNS:example.com,DNS:www.example.com"
openssl req -in example.csr -noout -text -verify # inspect and check the self-signatureFile formats
| Format | Encoding | Typical extensions | Holds |
|---|---|---|---|
| PEM | Base64 + header lines | .pem .crt .cer .key | One or more certs, or a key |
| DER | Raw binary ASN.1 | .der .cer | Exactly one cert or key |
| PKCS#7 (Cryptographic Message Syntax) | PEM or DER | .p7b .p7c | Certificates/chain only, no private key (common on Windows/Java) |
| PKCS#12 (Personal Information Exchange) | Binary, password-protected | .pfx .p12 | Private key + cert + chain in one bundle |
| JKS (Java KeyStore) | Java proprietary | .jks | Java keystore (PKCS#12 is now the Java default) |
openssl x509 -in cert.pem -outform der -out cert.der                    # PEM → DER
openssl x509 -in cert.der -inform der -out cert.pem                     # DER → PEM
openssl pkcs12 -export -inkey key.pem -in cert.pem -certfile chain.pem -out bundle.pfx
openssl pkcs12 -in bundle.pfx -nodes -out everything.pem                # PFX → PEM (key unencrypted!)
openssl pkcs7 -in chain.p7b -print_certs -out chain.pem # P7B → PEMInspecting real certificates
# Show the chain a server actually sends, with SNI
openssl s_client -connect example.com:443 -servername example.com -showcerts </dev/null

# Decode the leaf
openssl s_client -connect example.com:443 -servername example.com </dev/null 2>/dev/null \
| openssl x509 -noout -subject -issuer -dates -ext subjectAltName,basicConstraints,extendedKeyUsageBuilding a private CA (the lab version)
# 1. Root CA: self-signed, CA:TRUE, long-lived, keep offline
openssl req -x509 -new -newkey ec -pkeyopt ec_paramgen_curve:P-384 -nodes -days 3650 \
  -keyout root.key -out root.pem -subj "/CN=Lab Root CA" \
  -addext "basicConstraints=critical,CA:TRUE" -addext "keyUsage=critical,keyCertSign,cRLSign"

# 2. Issuing CA: signed by the root, pathlen:0 = may only sign leaves
openssl req -new -newkey ec -pkeyopt ec_paramgen_curve:P-256 -nodes \
  -keyout int.key -out int.csr -subj "/CN=Lab Issuing CA"
openssl x509 -req -in int.csr -CA root.pem -CAkey root.key -days 1825 -out int.pem \
  -extfile <(printf "basicConstraints=critical,CA:TRUE,pathlen:0\nkeyUsage=critical,keyCertSign,cRLSign")

# 3. Leaf: CA:FALSE, serverAuth, SANs
openssl x509 -req -in example.csr -CA int.pem -CAkey int.key -days 90 -out example.pem \
  -extfile <(printf "basicConstraints=critical,CA:FALSE\nkeyUsage=critical,digitalSignature\nextendedKeyUsage=serverAuth\nsubjectAltName=DNS:example.com,DNS:www.example.com")

openssl verify -CAfile root.pem -untrusted int.pem example.pem # → example.pem: OKCertificate Validation and Chains
Why there is a chain
Root CA keys are too valuable to use online, so roots sign a handful of intermediate (issuing) CAs, and those sign the end-entity ("leaf") certificates. If an intermediate is compromised, it can be revoked without replacing the root in every device on earth.
flowchart TB
  R["Root CA — self-signed<br/>lives in the client root store<br/>key kept offline in an HSM"]
  I1["Intermediate CA E6<br/>CA:TRUE, pathlen 0"]
  I2["Intermediate CA R11<br/>CA:TRUE, pathlen 0"]
  L1["Leaf: example.com<br/>CA:FALSE, EKU serverAuth"]
  L2["Leaf: api.example.net<br/>CA:FALSE, EKU serverAuth"]
  R --> I1 --> L1
  R --> I2 --> L2
The server sends leaf + intermediates (never needs to send the root: the client must already have it). The client builds a path from the leaf to any root it trusts and validates every link.
-
Issuer name and key identifier match the next certificate upLink
Subject of the issuer = Issuer of the child; AKI of the child = SKI of the issuer.
-
Signature verifies with the issuer's public keyLink
With an allowed algorithm: no MD5 or SHA-1 for certificate signatures; RSA ≥ 2048 bits.
-
Inside its validity periodLink
Every certificate in the path, including the intermediates.
-
Issuer is allowed to be an issuerLink
basicConstraints CA:TRUE,keyUsage keyCertSign, and the path length so far doesn't exceed anypathLenConstraintabove it. -
Names are inside any name constraintsLink
If an intermediate is constrained to
.corp.example, a leaf forbank.combelow it is invalid. -
Leaf-only checksLeaf
Hostname in SAN, EKU
serverAuth, not revoked, enough SCTs, lifetime within root-program limits.
Path building is harder than it looks
A newer root can be signed by an older, widely trusted root so old devices still trust it. That creates multiple valid paths, and the client must pick one that works.
When the cross-signing DST Root CA X3 expired (30 Sep 2021), clients with broken path building (old OpenSSL 1.0.x) picked the expired path and failed, even though a valid path via ISRG Root X1 existed.
Browsers often hide this misconfiguration by caching intermediates or fetching them via AIA. curl, Java, Go and mobile apps don't, so the same site "works in Chrome, fails in the API client".
Servers should send leaf first, then each issuer. Sending the root is harmless but wastes bytes. Sending an unrelated intermediate can confuse strict clients.
DV, OV and EV
| Type | What the CA verifies | How it shows | Notes |
|---|---|---|---|
| DV (Domain Validated) | You control the domain: HTTP file, DNS TXT record, or TLS-ALPN challenge, run automatically by ACME (Automatic Certificate Management Environment) | Padlock only | The vast majority of certificates; free and automated |
| OV (Organisation Validated) | DV + the organisation legally exists | Padlock only; org name visible in cert details | Policy OID 2.23.140.1.2.2 |
| EV (Extended Validation) | OV + stricter identity vetting | Was a green bar with the company name | Chrome 77 / Firefox 70 (2019) removed the EV UI: research showed users didn't notice its absence, and names could be registered to collide |
Memory hook"DV proves the domain, not the company." Every certificate proves control of a name. Only the name is cryptographically checked by the browser.
paypa1.comcan get a perfectly valid DV certificate. That's why phishing sites have padlocks, and why "look for the padlock" is no longer security advice.
Revocation
Last verified2026-10
What is this?Revocation is how a CA says "stop trusting this certificate before its expiry date", for example because the private key leaked or the certificate was mis-issued. It is the weakest part of web PKI: every mechanism has failed on privacy, reliability or scale, which is why the industry is moving to short-lived certificates instead.
| Method | How it works | Pros | Cons |
|---|---|---|---|
| CRL (Certificate Revocation List) | CA publishes a signed list of revoked serial numbers; client downloads it | Simple, cacheable | Lists grow large; refresh lag of hours to days |
| OCSP (Online Certificate Status Protocol, RFC 6960) | Client asks the CA's responder about one serial | Small, near real-time | Privacy leak (CA sees every site you visit); adds latency; usually soft-fail |
OCSP stapling (RFC 6066 status_request) | Server fetches its own signed OCSP response and sends it in the handshake | No privacy leak, no extra client round trip | Server must keep the staple fresh; clients still soft-fail if it's missing |
| OCSP Must-Staple (RFC 7633) | Cert extension: "reject me if there's no staple" | Turns soft-fail into hard-fail | Outages if the server's stapling breaks; rarely deployed |
| CRLSets (Chrome) | Google crawls CRLs and pushes a curated subset with browser updates | Local, private, fast | Only covers high-impact revocations, not every certificate |
| CRLite (Firefox) | Compresses all revocations of publicly trusted certs into a filter cascade, pushed daily | Complete, local, private | Browser-specific infrastructure |
| Short-lived certificates | Certificates expire before revocation would matter | No revocation infrastructure needed | Requires fully automated issuance (ACME) |
sequenceDiagram
  participant C as Client
  participant S as Server
  participant O as CA OCSP responder
  Note over S,O: Background, every few hours
  S->>O: OCSP request for my serial
  O-->>S: Signed response "good", valid for days
  Note over C,S: During the handshake
  C->>S: ClientHello + status_request
  S->>C: Certificate + stapled OCSP response
  Note over C: Verify CA signature<br/>on the staple. No call<br/>to the CA, no leak
ImportantThe soft-fail problemIf an OCSP check times out, almost every client continues rather than breaking the site. But an attacker who has a revoked certificate and sits on the network path can simply block the OCSP request. So plain OCSP stops nothing in exactly the scenario revocation exists for. (Adam Langley's classic line: soft-fail revocation is "like a seat belt that snaps when you crash".)
Where things stand (2026)The CA/Browser Forum made OCSP optional for CAs and requires CRLs. Let's Encrypt removed OCSP URLs from its certificates and shut its OCSP responders down in 2025. Browsers check revocation locally (CRLSets, CRLite). Maximum certificate lifetimes are being cut under ballot SC-081:
-
Until 15 March 2026Before398 days
Roughly 13 months, in force since 2020 (Apple led by policy, the Forum followed).
-
From 15 March 2026Now200 days
Domain-validation reuse also shrinks.
-
From 15 March 2027Next100 days
-
From 15 March 2029Final47 days
Domain-validation reuse drops to 10 days. Manual certificate renewal effectively stops being possible, so automation (ACME) becomes mandatory.
🎯On the job. Don't count on revocation to protect you from a leaked private key. Browsers mostly don't check OCSP live, and Let's Encrypt — the largest CA — ended its OCSP service in 2025 in favour of certificate revocation lists. The practical defence is short certificate lifetimes, so a stolen key stops working soon on its own; the CA/Browser Forum has voted to cut maximum public certificate lifetimes in steps to 47 days by 2029.
Cipher Suites
What is this?A cipher suite is a named bundle of algorithms the two sides agree to use. In TLS 1.2 the name spells out all four jobs: key exchange, authentication, bulk encryption, and the hash used for the PRF (pseudo-random function, TLS 1.2's key derivation) and MAC. TLS 1.3 slimmed it down to just the bulk cipher and hash, because key exchange and authentication are negotiated separately.
TLS_ECDHE_RSA_WITH_AES_256_GCM_SHA384
  │       │    │    │      │
  │       │    │    │      └── Hash for the PRF (and HMAC in non-AEAD suites)
  │       │    │    └────────── Symmetric cipher + mode
  │       │    └─────────────── Certificate / signature algorithm (authentication)
  │       └──────────────────── Key exchange
  └──────────────────────────── Protocol

TLS_AES_128_GCM_SHA256          ← TLS 1.3: only AEAD cipher + HKDF hash
The four components
RSA (client encrypts a secret to the server's key: no forward secrecy), DH/ECDH static (no FS), DHE/ECDHE ephemeral (fresh key per handshake: forward secrecy). TLS 1.3: (EC)DHE or PSK.
How the server proves its identity: RSA or ECDSA signature (TLS 1.3 adds Ed25519/Ed448), or a pre-shared key. anon (anonymous) suites have none and are trivially MITM'd.
AES-GCM and ChaCha20-Poly1305 (AEAD, preferred), AES-CCM (IoT); legacy AES-CBC + HMAC. Broken: RC4 (Rivest Cipher 4, a stream cipher with biased output), DES (Data Encryption Standard, 1977, 56-bit key, brute-forced in 1998) and 3DES (Triple DES, 64-bit blocks: Sweet32), export ciphers (deliberately weakened 40–56-bit crypto that 1990s US export law required), and NULL (no encryption at all).
SHA-256 or SHA-384 drives the PRF (1.2) or HKDF (1.3), and the HMAC in CBC suites. MD5 and SHA-1 suites are obsolete.
Forward secrecy, visually
Forward secrecy (often called "perfect forward secrecy", PFS) means that stealing the server's long-term private key later does not let you decrypt traffic you recorded earlier.
-
2026: an adversary records your encrypted TLS sessionsAttacker
They can't read them yet, but storage is cheap.
-
2028: the server's RSA private key leaksAttacker
Heartbleed-style bug, stolen backup, insider, or a legal order.
-
With RSA key exchange: every recorded session is now readableRSA kex
The pre-master secret was encrypted with that RSA key in each ClientKeyExchange. Decrypt it, re-derive the session keys, and read everything.
-
With ECDHE: nothing is recoverableECDHE
Each session's secret came from ephemeral DH keys that were thrown away after the handshake. The long-term key only signed the exchange. Stealing it lets you impersonate the server in future, but not decrypt the past.
Avoid, accept, prefer
| Verdict | TLS 1.2 suites | Why |
|---|---|---|
| Prefer | ECDHE-ECDSA-AES128-GCM-SHA256, ECDHE-RSA-AES128-GCM-SHA256, ECDHE-*-AES256-GCM-SHA384, ECDHE-*-CHACHA20-POLY1305 | Forward secrecy + AEAD |
| Accept (legacy clients only) | ECDHE-*-AES128-CBC-SHA256, DHE-RSA-AES128-GCM-SHA256 (≥ 2048-bit group) | FS but CBC (timing-attack history) or slow/weak-group DHE |
| Avoid | RSA-kex suites (AES128-GCM-SHA256, etc.), anything with CBC-SHA (SHA-1 HMAC) on new deployments | No forward secrecy; ROBOT-style oracles; Lucky13 |
| Never | RC4, 3DES/DES, EXPORT, NULL, anon, MD5 | Broken: RC4 biases, Sweet32, FREAK/Logjam, no encryption, no authentication |
TLS 1.3 needs no such table. It defines only five suites, all AEAD:
| Suite | Code | Use |
|---|---|---|
TLS_AES_128_GCM_SHA256 | 0x1301 | Default everywhere; mandatory to implement |
TLS_AES_256_GCM_SHA384 | 0x1302 | Common; required by some compliance regimes |
TLS_CHACHA20_POLY1305_SHA256 | 0x1303 | Fast without AES hardware (older phones, embedded) |
TLS_AES_128_CCM_SHA256 | 0x1304 | IoT / constrained devices |
TLS_AES_128_CCM_8_SHA256 | 0x1305 | IoT only: CCM_8 means an 8-byte tag instead of 16, so forgeries are easier; not for the web |
Enumerating what a server supports
nmap --script ssl-enum-ciphers -p 443 example.com        # graded list per protocol version
testssl.sh --protocols --ciphers --vulnerable example.com
openssl s_client -connect example.com:443 -tls1_2 -cipher 'ECDHE-RSA-AES128-GCM-SHA256'   # does this one work?
openssl s_client -connect example.com:443 -tls1_3 -ciphersuites TLS_CHACHA20_POLY1305_SHA256TipIn TLS 1.2 the server usually decides from the client's list (with "server cipher preference" enabled). Modern guidance (Mozilla "intermediate") lets the client pick among AEAD suites: a phone without AES hardware will choose ChaCha20, which is faster for it.
The Record Layer
What is this?Everything TLS sends — handshake messages, alerts, application data — is wrapped in records. The record layer splits data into chunks of up to 16 KB, protects each chunk with the current keys, and tags it with a content type.
- Content type
- 20 change_cipher_spec · 21 alert · 22 handshake · 23 application_data · 24 heartbeat
- Version
- 0x0303 for TLS 1.2 and (frozen) for TLS 1.3; 0x0301 allowed in the first ClientHello
- Length
- Up to 2^14 (16,384) bytes of plaintext; up to 2^14 + 256 of ciphertext in TLS 1.3
- Fragment
- The payload: plaintext before keys exist, ciphertext + tag afterwards
Handshake messages have their own small header inside handshake records. One handshake message can span several records, and one record can carry several handshake messages.
- msg_type
- 1 ClientHello · 2 ServerHello · 4 NewSessionTicket · 8 EncryptedExtensions · 11 Certificate · 12 ServerKeyExchange · 13 CertificateRequest · 14 ServerHelloDone · 15 CertificateVerify · 16 ClientKeyExchange · 20 Finished · 24 KeyUpdate
- length
- Length of the message body (up to 16 MB)
- body
- The message itself
What you'd see in a hex dump of a ClientHello:
16 03 01 02 00   01 00 01 fc   03 03   a3 4f 9c ... (32 random bytes)
│  │     │       │  │          │
│  │     │       │  │          └─ legacy_version 0x0303
│  │     │       │  └──────────── handshake length 0x0001fc = 508
│  │     │       └─────────────── msg_type 1 = ClientHello
│  │     └─────────────────────── record length 0x0200 = 512
│  └───────────────────────────── record version 0x0301 (compat value)
└──────────────────────────────── content type 0x16 = 22 = handshake
TLS 1.3 hides the real content type
- Outer type
- Always 23 (application_data) once keys are in use
- Version
- Always 0x0303
- Length
- Ciphertext length
- Encrypted: content
- Handshake, alert or application data
- Encrypted: real type
- The true content type, inside the encryption
- Encrypted: padding
- Optional zeros to hide the true length
- AEAD tag
- Authenticates everything (header bytes are the additional data)
The nonce for each record is the per-direction IV XORed with a 64-bit sequence number that both sides count but never send. Drop, replay or reorder a record and the tag check fails. This is TLS's anti-replay mechanism within a connection.
Alerts
Alerts are two bytes: level (1 warning, 2 fatal) and description. In TLS 1.3 everything except close_notify and user_canceled is fatal.
| Code | Alert | Usually means |
|---|---|---|
| 0 | close_notify | Clean shutdown. Missing it allows truncation attacks |
| 10 | unexpected_message | State machine violation |
| 20 | bad_record_mac | Decryption/tag failure: tampering or a key mismatch |
| 40 | handshake_failure | No common parameters |
| 42 / 45 / 48 | bad_certificate / certificate_expired / unknown_ca | Peer rejected the certificate |
| 70 | protocol_version | No common TLS version |
| 71 | insufficient_security | Offered parameters too weak |
| 86 | inappropriate_fallback | Downgrade attempt detected (TLS_FALLBACK_SCSV, "Signaling Cipher Suite Value") |
| 112 | unrecognized_name | No certificate for that SNI |
| 116 | certificate_required | mTLS server got no client certificate (1.3) |
| 120 | no_application_protocol | ALPN mismatch |
The TLS 1.2 Handshake
With RSA key exchange (no forward secrecy)
sequenceDiagram
  autonumber
  participant C as Client
  participant S as Server
  C->>S: ClientHello<br/>version, client random, suites, extensions
  S->>C: ServerHello<br/>chosen suite, server random, session ID
  S->>C: Certificate (RSA public key)
  S->>C: ServerHelloDone
  Note over C: Pick 48-byte<br/>pre-master secret,<br/>encrypt to RSA key
  C->>S: ClientKeyExchange (encrypted pre-master)
  C->>S: ChangeCipherSpec
  C->>S: Finished (encrypted)
  S->>C: ChangeCipherSpec
  S->>C: Finished (encrypted)
  Note over C,S: 2 round trips before application data
With ECDHE (forward secrecy)
sequenceDiagram
  autonumber
  participant C as Client
  participant S as Server
  C->>S: ClientHello<br/>suites, supported_groups, sig algs
  S->>C: ServerHello (ECDHE_RSA suite)
  S->>C: Certificate
  S->>C: ServerKeyExchange<br/>curve + ephemeral public key<br/>signed with cert private key
  S->>C: ServerHelloDone
  Note over C: Verify signature,<br/>make own ephemeral<br/>key, derive secret
  C->>S: ClientKeyExchange (client ephemeral public key)
  C->>S: ChangeCipherSpec + Finished
  S->>C: ChangeCipherSpec + Finished
The signature in ServerKeyExchange is the authentication. It covers both randoms and the server's DH public key, so an attacker can't swap in their own DH key without the certificate's private key.
From secret to keys (TLS 1.2)
-
Pre-master secretSecret
RSA: 48 random bytes chosen by the client. ECDHE: the shared x-coordinate.
-
Master secret = PRF(pre-master, "master secret", client_random + server_random)PRF48 bytes
With the Extended Master Secret extension (RFC 7627) the seed is the session hash instead, which binds the master secret to the whole handshake (fixes the Triple Handshake attack).
-
Key block = PRF(master, "key expansion", server_random + client_random)PRF
Sliced into client/server MAC keys (CBC suites), client/server encryption keys, and client/server IVs.
-
Finished = PRF(master, "client finished" or "server finished", hash(all handshake messages))Check12 bytes
Proves both sides saw the same handshake and derived the same keys.
Session resumption
A full handshake costs 2 round trips plus public-key operations. Resumption reuses the master secret from an earlier session in an abbreviated handshake (1 round trip, no certificate, no key exchange).
The server keeps a cache of master secrets keyed by a session ID. The client sends the ID in its next ClientHello. Hard to scale across a server fleet (shared cache needed).
The server encrypts the session state with a ticket key only it knows, and hands the blob to the client. Stateless for the server, but the ticket key becomes a crown jewel: whoever steals it can decrypt every session resumed with it, which breaks forward secrecy until the key is rotated.
sequenceDiagram
  participant C as Client
  participant S as Server
  C->>S: ClientHello + session ticket (or session ID)
  S->>C: ServerHello (same session)
  S->>C: ChangeCipherSpec + Finished
  C->>S: ChangeCipherSpec + Finished
  Note over C,S: 1 RTT, no Certificate, no key exchange
Mutual TLS (client certificates)
sequenceDiagram
  autonumber
  participant C as Client
  participant S as Server
  C->>S: ClientHello
  S->>C: ServerHello, Certificate, ServerKeyExchange
  S->>C: CertificateRequest<br/>acceptable CAs + sig algs
  S->>C: ServerHelloDone
  C->>S: Certificate (client cert, in the clear in 1.2)
  C->>S: ClientKeyExchange
  C->>S: CertificateVerify<br/>signature over handshake so far
  C->>S: ChangeCipherSpec + Finished
  S->>C: ChangeCipherSpec + Finished
WarningIn TLS 1.2 the client certificate is sent unencrypted, so a passive observer learns the client's identity (name, email, device ID). TLS 1.3 encrypts it. This matters for mTLS-based device identity and zero-trust deployments.
Renegotiation
TLS 1.2 allowed a new handshake inside an existing connection, used for "this URL needs a client certificate" or rekeying. It caused CVE-2009-3555 (see attacks below) and DoS issues. The renegotiation_info extension (RFC 5746) fixed the injection flaw. TLS 1.3 removed renegotiation entirely.
TLS Extensions
Extensions are typed fields at the end of ClientHello/ServerHello that let TLS grow without new versions. Each side ignores extension types it doesn't recognise, which is what makes them safe to add. A server may only send an extension the client offered.
| Extension (code) | What it does | Security note |
|---|---|---|
server_name (0) | SNI: which hostname the client wants | Plaintext before ECH; used by censors and firewalls |
status_request (5) | Ask the server to staple OCSP | Privacy-preserving revocation |
supported_groups (10) | Curves / DH groups offered | Dropping weak groups stops Logjam-style downgrades |
signature_algorithms (13) | Which signature + hash combos are acceptable | Prevents being forced into SHA-1 or PKCS#1 v1.5 |
application_layer_protocol_negotiation (16) | ALPN: h2, http/1.1, … | Prevents cross-protocol attacks (ALPACA) when enforced |
signed_certificate_timestamp (18) | Deliver CT SCTs in the handshake | Alternative to embedding SCTs in the cert |
encrypt_then_mac (22) | MAC the ciphertext, not the plaintext, in CBC suites | Kills padding-oracle classes (RFC 7366) |
extended_master_secret (23) | Bind master secret to the session hash | Fixes Triple Handshake (RFC 7627) |
session_ticket (35) | Stateless resumption | Ticket key compromise breaks FS |
heartbeat (15) | Keep-alive for DTLS | The extension Heartbleed lived in; disable it |
renegotiation_info (65281) | Bind renegotiations to the previous handshake | Fix for CVE-2009-3555 |
One IP can host thousands of HTTPS sites because the server reads SNI to pick the certificate. No SNI → default certificate → name mismatch. Firewalls and CDNs route and filter on SNI, and domain fronting abused the gap between SNI and the HTTP Host header.
Configure the server (ssl_stapling on in nginx) and check with openssl s_client -status. Look for OCSP Response Status: successful.
Rotate ticket keys often (hours), share them securely across the fleet, and never persist them to disk. A ticket key that lives for months quietly turns months of traffic into one decryptable archive.
Decrypting and Inspecting TLS
There are exactly two ways to read TLS traffic you captured: have the session keys, or be in the middle of the connection.
Load the server's private key into Wireshark; it decrypts each ClientKeyExchange to get the pre-master secret. Useless against ECDHE and TLS 1.3 — the private key never touched the session secret.
Browsers, curl and most TLS libraries write per-session secrets when SSLKEYLOGFILE is set. Wireshark reads the file and decrypts everything, including TLS 1.3 and QUIC.
A proxy terminates TLS with its own certificate (trusted via an installed root) and opens a second TLS connection to the real server. Used by corporate inspection, Burp, mitmproxy — and by malware.
EDR (endpoint detection and response) agents or eBPF hooks read plaintext before encryption (e.g. uprobes on SSL_write). No crypto broken, but full visibility on that host.
# SSLKEYLOGFILE format (NSS key log) — one line per secret
CLIENT_RANDOM                    <client_random_hex> <master_secret_hex>      ← TLS 1.2
CLIENT_HANDSHAKE_TRAFFIC_SECRET  <client_random_hex> <secret_hex>             ← TLS 1.3
SERVER_HANDSHAKE_TRAFFIC_SECRET  <client_random_hex> <secret_hex>
CLIENT_TRAFFIC_SECRET_0          <client_random_hex> <secret_hex>
SERVER_TRAFFIC_SECRET_0          <client_random_hex> <secret_hex>
EXPORTER_SECRET <client_random_hex> <secret_hex>SSLKEYLOGFILE=$HOME/tls-keys.log curl -s https://example.com -o /dev/null
# Wireshark: Preferences → Protocols → TLS → (Pre)-Master-Secret log filename
# Useful display filters:
# tls.handshake.type == 1 ClientHellos
# tls.handshake.extensions_server_name == "example.com"
# tls.record.content_type == 21 alerts
# tls.handshake.ja4 JA4 fingerprints (recent Wireshark)CautionA key log file is the session's crown jewels. Malware that sets
SSLKEYLOGFILEsystem-wide gets silent decryption of every browser session. Hunt for that environment variable on endpoints, and never leave it set on a workstation after debugging.
TLS Defenses: HSTS, CAA and Certificate Transparency
HSTS (HTTP Strict Transport Security, RFC 6797)
Strict-Transport-Security: max-age=63072000; includeSubDomains; preloadHow long (seconds) the browser must use HTTPS only for this host. Two years is the preload requirement.
Applies the policy to every subdomain. Dangerous if any internal subdomain can't do HTTPS.
Consent to be hard-coded into browsers' preload list (hstspreload.org), which removes the first-visit gap.
Under HSTS, certificate errors have no "proceed anyway" button: users can't click through a MITM warning.
HPKP (HTTP Public Key Pinning, RFC 7469) tried to go further by pinning keys, but sites bricked themselves and attackers could pin hostile keys ("ransom pinning"). Chrome removed it in 2018–2019. Certificate Transparency replaced pinning as the web's defence against rogue certificates.
CAA (Certification Authority Authorization, RFC 8659)
A DNS record that says which CAs may issue for your domain. Since September 2017 every public CA must check it before issuing.
example.com.  CAA 0 issue     "letsencrypt.org"                 ; only Let's Encrypt may issue
example.com.  CAA 0 issuewild ";"                               ; nobody may issue wildcards
example.com.  CAA 0 iodef     "mailto:security@example.com"     ; report violations here
example.com.  CAA 0 issue     "letsencrypt.org; accounturi=https://acme-v02.api.letsencrypt.org/acme/acct/123"   ; RFC 8657: only *our* account
CAA is a check on honest CAs, not on attackers: a compromised CA can ignore it. Combine it with CT monitoring.
Certificate Transparency (RFC 6962, v2 RFC 9162)
What is this?A set of public, append-only logs that every publicly trusted certificate must be submitted to. Anyone can search them, so a domain owner can see every certificate ever issued for their names. Browsers refuse certificates that can't prove they were logged.
-
CA builds a precertificateCA
The final certificate plus a "poison" extension that makes it unusable for TLS.
-
Submit to several independent logsCT logs
Each log returns an SCT (Signed Certificate Timestamp): a signed promise to add it within the Maximum Merge Delay (24 h).
-
Embed the SCTs and issue the real certificateCA
SCTs can also be delivered via the TLS extension or a stapled OCSP response.
-
Browser checks the SCTsBrowser
Valid signatures from logs it trusts, from distinct operators. Chrome requires 2 or 3 depending on lifetime.
-
Monitors watch the logsMonitors
Domain owners (or services such as crt.sh, Cloudflare, Facebook) alert on unexpected certificates for their names.
-
Auditors check the logs are honestAuditors
Inclusion proofs (is this cert in the tree?) and consistency proofs (did the log only append?).
Why a Merkle tree?The log is a binary hash tree. Each leaf is a hash of one certificate, and each parent is the hash of its two children. The root hash (signed as the Signed Tree Head, STH) commits to every entry.
                    Root = H(H12 ‖ H34)          ← signed tree head (STH)
                   /                   \
           H12 = H(H1 ‖ H2)      H34 = H(H3 ‖ H4)
            /        \             /        \
         H1          H2         H3          H4
       cert A      cert B     cert C      cert D

Inclusion proof for cert C: give the client H4 and H12.
  Client computes H3 = hash(C) → H34 = H(H3 ‖ H4) → Root = H(H12 ‖ H34), compares with the signed STH.
  Proof size = log2(n) hashes: ~20-30 hashes even for a billion certificates.

Consistency proof: shows tree of size 4 is a prefix of tree of size 8, i.e. the log only appended
and never rewrote history.
Memory hook"CT doesn't prevent mis-issuance; it makes it impossible to hide." A rogue CA can still sign a certificate for your domain. But to be accepted by browsers it has to be logged publicly, and your monitor fires within hours. DigiNotar (2011) went undetected for weeks. Under CT, the same attack is visible to the world.
Major TLS Attacks and Failures
Each of these broke something specific, and each fix is now a rule in modern configs.
| Year | Attack | CVE | What broke | Fix |
|---|---|---|---|---|
| 2009 | Insecure renegotiation | CVE-2009-3555 | Attacker's data spliced before the victim's renegotiated session | renegotiation_info (RFC 5746); removed in 1.3 |
| 2011 | BEAST | CVE-2011-3389 | Predictable CBC IVs in TLS 1.0 let a chosen-plaintext attacker decrypt cookies | TLS 1.1+ explicit IVs, 1/n-1 record splitting |
| 2012 | CRIME | CVE-2012-4929 | TLS compression leaked secrets through ciphertext length | Disable TLS compression (removed in 1.3) |
| 2013 | BREACH | CVE-2013-3587 | Same idea via HTTP-level gzip | Don't compress secrets with attacker input; token masking |
| 2013 | Lucky13 | CVE-2013-0169 | Timing side channel in CBC MAC-then-encrypt padding checks | Constant-time code; AEAD suites |
| 2013–15 | RC4 biases | — | Statistical keystream biases recover plaintext | RC4 prohibited (RFC 7465) |
| 2014 | Heartbleed | CVE-2014-0160 | OpenSSL heartbeat over-read leaked up to 64 KB of memory: keys, cookies | Patch, revoke and reissue certificates, rotate keys |
| 2014 | POODLE | CVE-2014-3566 | SSL 3.0 CBC padding not checked; downgrade dance forced SSL 3.0 | Disable SSL 3.0; TLS_FALLBACK_SCSV |
| 2014 | Triple Handshake | — | Resumption + renegotiation let a MITM sync master secrets across connections | Extended Master Secret (RFC 7627) |
| 2015 | FREAK | CVE-2015-0204 | Clients accepted 512-bit export RSA when not asked | Remove export suites |
| 2015 | Logjam | CVE-2015-4000 | Downgrade to 512-bit export DHE; precomputation on common 1024-bit groups | ≥ 2048-bit DH groups, prefer ECDHE |
| 2016 | DROWN | CVE-2016-0800 | SSLv2 on any server sharing the RSA key enabled decryption of TLS sessions | Disable SSLv2 everywhere; don't share keys |
| 2016 | Sweet32 | CVE-2016-2183 | 64-bit block ciphers (3DES) collide after ~32 GB (birthday bound) | Remove 3DES |
| 2017 | ROBOT | CVE-2017-13099 et al. | Bleichenbacher padding oracle in RSA key exchange, still alive 19 years later | Disable RSA key exchange |
| 2020 | Raccoon | CVE-2020-1968 | Timing leak from leading-zero stripping of DH secrets | Ephemeral, never-reused DH keys; TLS 1.3 |
| 2021 | ALPACA | — | Cross-protocol: redirect HTTPS traffic to an FTP/SMTP server sharing the certificate | Strict ALPN and SNI checking |
The attack names, decoded
Most of these names are backronyms. Knowing what each stands for is a quick way to remember what it broke:
Browser Exploit Against SSL/TLS: guessed CBC IVs in TLS 1.0 let injected JavaScript decrypt cookies byte by byte.
Compression Ratio Info-leak Made Easy: compressed size reveals how much of an attacker's guess matches a secret.
Browser Reconnaissance and Exfiltration via Adaptive Compression of Hypertext: CRIME moved up to HTTP gzip.
Named after the 13 bytes of TLS header fed into the MAC, which made the timing difference measurable.
Padding Oracle On Downgraded Legacy Encryption: force SSL 3.0, then abuse its unchecked CBC padding.
Factoring RSA Export Keys: trick clients into 512-bit export RSA, which can be factored in hours.
Not an acronym: the same downgrade idea for Diffie–Hellman, to 512-bit export groups.
Decrypting RSA with Obsolete and Weakened eNcryption: use an SSLv2 server sharing your key as a decryption oracle.
Birthday attack on 64-bit block ciphers: blocks repeat after about 2³² blocks (32 GB), leaking data.
Return Of Bleichenbacher's Oracle Threat: the 1998 RSA padding oracle, found alive in 2017 products.
Timing differences from leading zero bytes in a DH secret leak enough to attack static DH.
Application Layer Protocols Allowing Cross-Protocol Attacks: redirect HTTPS to another service sharing the certificate.
Named after the TLS heartbeat extension it lived in; it "bled" server memory.
Insecure renegotiation, step by step
sequenceDiagram
  participant V as Victim client
  participant A as Attacker (MITM)
  participant S as Server
  A->>S: Full TLS handshake (as the attacker)
  A->>S: "GET /transfer?to=attacker" + "X-Ignore: " (no newline)
  V->>A: ClientHello (victim starts TLS)
  A->>S: Forwards it as a RENEGOTIATION in the attacker's session
  S-->>V: Handshake completes, encrypted end to end with the victim
  V->>S: "GET /home" + victim's cookie
  Note over S: Server sees ONE<br/>request: attacker's<br/>line + victim's<br/>cookie
The server glued the attacker's plaintext prefix onto the victim's authenticated request, because nothing tied the renegotiated handshake to the connection it happened inside. RFC 5746 fixed this by making each renegotiation include the previous handshake's Finished values.
Compression, renegotiation, export suites, SSLv2 compatibility, heartbeat: almost every major attack lived in a feature most deployments didn't need.
FREAK, Logjam, POODLE and DROWN all forced a connection onto the weakest thing both sides still supported. Removing weak options beats negotiating safely around them.
Padding oracles and timing leaks kept recurring until AEAD made encryption and authentication one operation.
Heartbleed needed no cryptanalysis, just a missing bounds check. Memory-safe TLS stacks (rustls, Go) are partly a response.
📰Real incident — Heartbleed (2014, CVE-2014-0160). A missing length check in OpenSSL's heartbeat feature let anyone ask a server to send back up to 64 KB of its memory, repeatedly and without leaving a log entry. That memory could contain private keys, session cookies, and passwords. The Canada Revenue Agency reported that about 900 social insurance numbers were stolen through it within days of disclosure. Patching was not enough: every exposed server also had to replace its certificate and private key and invalidate sessions.
TLS 1.3: What Changed and Why
What is this?TLS 1.3 (RFC 8446, 2018) is less an upgrade than a cleanup. It removes every feature that produced a major attack, makes forward secrecy mandatory, encrypts most of the handshake, and cuts a full handshake to one round trip.
RSA key exchange, static DH, CBC, RC4, 3DES, SHA-1/MD5 in signatures, compression, renegotiation, custom DHE groups, ChangeCipherSpec, DSA, export suites.
Full handshakes always use (EC)DHE. Resumption can still use (EC)DHE with the PSK (psk_dhe_ke).
Everything after ServerHello is encrypted, including the server certificate and (for mTLS) the client certificate.
The client sends its key share in the first message. Resumed sessions can send data in the first flight (0-RTT).
HKDF-based key schedule with separate secrets per phase, replacing the 1.2 PRF.
CertificateVerify signs a hash of the entire handshake, not just the key exchange parameters (1.2's weakness exploited by Logjam-style attacks).
TLS 1.2 vs TLS 1.3
| Feature | TLS 1.2 | TLS 1.3 |
|---|---|---|
| Handshake RTT | 2 (1 with resumption) | 1 (0 with 0-RTT) |
| Forward secrecy | Optional | Mandatory (full handshakes) |
| Cipher suites | 300+ defined (including weak) | 5, all AEAD |
| Suite name covers | Kex + auth + cipher + hash | Cipher + hash only |
| Certificate in handshake | Plaintext | Encrypted |
| Client certificate (mTLS) | Plaintext | Encrypted |
| RSA key transport | Allowed | Removed |
| RC4, 3DES, CBC, export ciphers | Allowed | Removed |
| Compression / renegotiation | Allowed | Removed (KeyUpdate + post-handshake auth instead) |
| Downgrade protection | Weak (Finished only, SCSV) | Transcript signature + ServerHello.random sentinel |
| Key derivation | PRF(master_secret) | HKDF key schedule |
| Session resumption | Session IDs / tickets | PSK (tickets carry PSK identities) |
| Record content type | Plaintext | Hidden inside encryption |
Memory hookTLS 1.3 is 1-RTT because the client "guesses" and is almost always right. In TLS 1.2 the client first asks which key-exchange to use, waits, then sends its key — two round trips of negotiating. TLS 1.3 collapses this: there's only one key-exchange family (ECDHE), so the client just sends its ECDHE key share in the very first message (the ClientHello) without asking. The server replies with its own share and is already able to encrypt the certificate. Mnemonic: 1.2 negotiates-then-acts; 1.3 acts immediately because there's nothing left to negotiate. That same "send key share upfront" is also why the certificate is now encrypted (a passive eavesdropper can't see which site you visited from the cert) and why forward secrecy is automatic (ECDHE every time, RSA key transport deleted).
The full handshake
sequenceDiagram
  autonumber
  participant C as Client
  participant S as Server
  C->>S: ClientHello<br/>supported_versions, key_share,<br/>signature_algorithms, SNI, ALPN
  S->>C: ServerHello<br/>key_share, supported_versions
  Note over C,S: Handshake keys derived — all below is encrypted
  S->>C: EncryptedExtensions (ALPN, ...)
  S->>C: CertificateRequest (only for mTLS)
  S->>C: Certificate
  S->>C: CertificateVerify
  S->>C: Finished
  Note over S: May already send<br/>data (0.5-RTT)
  C->>S: Certificate + CertificateVerify (only for mTLS)
  C->>S: Finished
  Note over C,S: Application traffic keys in use
  S-->>C: NewSessionTicket (any time after)
When the client guessed wrong: HelloRetryRequest
If the client's key share is for a group the server won't use (say the client sent only X25519MLKEM768 and the server only does P-256), the server replies with a HelloRetryRequest. It's a ServerHello whose random field is the fixed value SHA-256("HelloRetryRequest"). The cost is one extra round trip.
sequenceDiagram
  participant C as Client
  participant S as Server
  C->>S: ClientHello, key_share X25519MLKEM768
  S->>C: HelloRetryRequest<br/>"use secp256r1" + cookie
  C->>S: ClientHello again<br/>key_share secp256r1 + cookie
  S->>C: ServerHello ... Finished
  C->>S: Finished
The cookie extension lets the server stay stateless during the retry (useful against DoS, and essential in DTLS/QUIC).
Renegotiation is gone — what replaced it
Either side can send a KeyUpdate message to roll its sending keys forward (traffic_secret_N+1 = HKDF-Expand-Label(secret_N, "traffic upd", "", L)). Used for long-lived connections; no new handshake.
If the client advertised post_handshake_auth, the server can send a CertificateRequest later in the connection (e.g. when the user reaches /admin). HTTP/2 forbids it, so in practice it's used with HTTP/1.1.
Middleboxes, GREASE and the version number that lies
When TLS 1.3 was tested on the real internet, a few percent of connections failed because firewalls and inspection boxes choked on anything unfamiliar. The fix was to make TLS 1.3 look like a TLS 1.2 session resumption:
Record version and legacy_version stay 0x0303 (TLS 1.2). The real version is negotiated in the supported_versions extension.
The client sends a random 32-byte legacy_session_id and the server echoes it, as in 1.2 resumption.
Both sides may send a meaningless CCS record, which middleboxes expect to see (RFC 8446 appendix D.4, "middlebox compatibility mode").
Clients sprinkle random reserved values into cipher, extension, group and version lists. Servers that crash on unknown values get caught now, so the protocol stays extensible ("don't let the joints rust").
Downgrade protectionA TLS 1.3 server forced down to TLS 1.2 puts the bytes 44 4F 57 4E 47 52 44 01 ("DOWNGRD\x01") at the end of ServerHello.random (...00 for TLS 1.1 or lower). The random is covered by the signature, so an attacker can't remove it, and a 1.3-capable client that sees it aborts.
Forward secrecy and the visibility debate
Mandatory forward secrecy broke a long-standing enterprise practice: passive decryption by loading the server's RSA private key into a monitoring appliance. With ECDHE there's nothing to load. Organisations now choose between:
A load balancer or proxy ends TLS, inspects, and starts a new TLS connection. The usual answer.
Servers log session secrets (key log format) to a secure collector. Works, but key handling is now your problem.
EDR / eBPF reads plaintext on the host.
ETSI's (European Telecommunications Standards Institute) Enterprise Transport Security (ETS, formerly eTLS) reuses a static DH key to restore passive decryption. The IETF rejected the idea; it deliberately removes forward secrecy.
Decrypting TLS 1.3
The only options are the key log file or being an active MITM. The RSA-private-key trick does not work, not even with an RSA certificate, because RSA only signs in TLS 1.3.
TLS 1.3 Under the Hood
The key schedule
TLS 1.3 derives every key from three chained secrets using HKDF (RFC 5869). HKDF-Extract concentrates entropy into a fixed-size secret. HKDF-Expand-Label stretches a secret into labelled outputs (all labels are prefixed with "tls13 "). Each stage mixes in new input and hashes of the handshake transcript so far.
        PSK (or zeros)
             │
  0 ──▶ HKDF-Extract ══▶ EARLY SECRET ──┬──▶ binder_key
             │                          ├──▶ client_early_traffic_secret     ← 0-RTT
             │                          └──▶ early_exporter_master_secret
             ▼
      Derive-Secret("derived")
             │
 (EC)DHE ─▶ HKDF-Extract ══▶ HANDSHAKE SECRET ──┬──▶ client_handshake_traffic_secret
             │                                  └──▶ server_handshake_traffic_secret
             ▼
      Derive-Secret("derived")
             │
  0 ──▶ HKDF-Extract ══▶ MASTER SECRET ──┬──▶ client_application_traffic_secret_0
                                         ├──▶ server_application_traffic_secret_0
                                         ├──▶ exporter_master_secret
└──▶ resumption_master_secret| Secret | HKDF label | Transcript hashed in | Protects |
|---|---|---|---|
| binder_key | ext binder / res binder | (empty) | PSK binder in the ClientHello |
| client_early_traffic_secret | c e traffic | ClientHello | 0-RTT early data |
| client / server handshake traffic | c hs traffic / s hs traffic | ClientHello … ServerHello | EncryptedExtensions → Finished |
| client / server application traffic | c ap traffic / s ap traffic | ClientHello … server Finished | All application data |
| exporter_master_secret | exp master | ClientHello … server Finished | Keying material for applications |
| resumption_master_secret | res master | ClientHello … client Finished | PSKs in future NewSessionTickets |
Derive-Secret(Secret, Label, Messages) = HKDF-Expand-Label(Secret, Label, Transcript-Hash(Messages), Hash.length), and every label is prefixed with "tls13 " on the wire.
-
write_key = HKDF-Expand-Label(traffic_secret, "key", "", key_length)Keys
16 bytes for AES-128-GCM, 32 for AES-256-GCM / ChaCha20.
-
write_iv = HKDF-Expand-Label(traffic_secret, "iv", "", 12)Keys
-
per-record nonce = write_iv XOR (64-bit sequence number, left-padded)Nonce
Unique for every record without sending anything; the sequence number resets to 0 when keys change.
-
AEAD-Encrypt(write_key, nonce, additional_data = record header, plaintext = content ‖ type ‖ padding)Seal
What the signatures and MACs cover
Signature over: 64 bytes of 0x20, the string "TLS 1.3, server CertificateVerify", a 0x00 byte, then the transcript hash up to the Certificate. The fixed prefix stops a signature from being reused in another context (or by TLS 1.2).
finished_key = HKDF-Expand-Label(handshake_traffic_secret, "finished", "", Hash.length), then verify_data = HMAC(finished_key, transcript hash). Proves key possession and that both sides saw identical messages.
exporter_master lets applications derive extra keying material bound to the session (RFC 5705/8446), e.g. for token binding or channel binding in authentication protocols.
Session resumption with PSKs
After the handshake the server sends one or more NewSessionTicket messages. Each ticket identifies a PSK derived from resumption_master_secret. The ticket blob itself is opaque to the client: usually the server's encrypted session state.
- ticket_lifetime
- Seconds the ticket may be used; at most 604,800 (7 days)
- ticket_age_add
- Random value added to the client's reported ticket age, so passive observers can't link resumptions by age
- ticket_nonce
- Makes each ticket's PSK unique: PSK = HKDF-Expand-Label(resumption_master, "resumption", nonce, L)
- ticket
- The opaque identity the client sends back (often server-encrypted state)
- extensions
- e.g. early_data with max_early_data_size (0-RTT allowed)
sequenceDiagram
  autonumber
  participant C as Client
  participant S as Server
  C->>S: ClientHello<br/>key_share + psk_key_exchange_modes psk_dhe_ke<br/>pre_shared_key (ticket identity + binder)
  S->>C: ServerHello<br/>pre_shared_key (selected) + key_share
  S->>C: EncryptedExtensions
  S->>C: Finished
  C->>S: Finished
  Note over C,S: No Certificate / CertificateVerify<br/>PSK proves identity, (EC)DHE keeps forward secrecy
Resume with the PSK alone. Cheapest, but the session keys depend only on the PSK: no forward secrecy for the resumed session if the ticket key leaks.
PSK + a fresh (EC)DHE exchange. Forward secrecy preserved. What browsers use.
An HMAC over the ClientHello (minus the binders) keyed from the PSK. Proves the client really holds the PSK and binds it to this exact hello. pre_shared_key must be the last extension because of it.
0-RTT early data
A returning client can encrypt application data with client_early_traffic_secret (derived from the PSK) and send it in the same flight as the ClientHello.
sequenceDiagram
  autonumber
  participant C as Client
  participant S as Server
  C->>S: ClientHello + early_data + pre_shared_key
  C->>S: Early data: GET /home (0-RTT keys)
  S->>C: ServerHello + EncryptedExtensions (early_data accepted)
  S->>C: Finished
  S-->>C: Response to GET /home (0.5-RTT)
  C->>S: EndOfEarlyData + Finished
Caution0-RTT data can be replayedIt's encrypted under keys derived only from the PSK and the ClientHello, with no fresh server input. An attacker can capture that first flight and send it again, to the same server or another node in the fleet. It also has no forward secrecy against PSK compromise.
The server remembers which tickets were used and rejects repeats. Hard across a global fleet.
Remember recent ClientHello randoms within a time window and reject duplicates.
Reject early data whose obfuscated ticket age doesn't match expectations (limits the replay window).
Only accept 0-RTT for safe, idempotent requests (GET without side effects). CDNs mark requests with Early-Data: 1, and origins can answer 425 Too Early (RFC 8470) to force a retry after the handshake.
Mutual TLS in 1.3
The server's CertificateRequest comes inside the encrypted flight, and the client's Certificate + CertificateVerify are encrypted too, so a passive observer no longer learns client identities. The request can carry signature_algorithms, certificate_authorities (acceptable CAs) and oid_filters (required certificate extensions). A client with no suitable certificate sends an empty Certificate; the server decides whether to abort (certificate_required, alert 116).
TLS 1.3 Extensions
In TLS 1.3, extensions carry most of the negotiation, and each extension may only appear in specific messages: CH (ClientHello), SH (ServerHello), EE (EncryptedExtensions), CT (Certificate), CR (CertificateRequest), NST (NewSessionTicket), HRR (HelloRetryRequest).
| Extension (code) | Appears in | Purpose |
|---|---|---|
supported_versions (43) | CH, SH, HRR | The real version negotiation (0x0304) |
key_share (51) | CH, SH, HRR | (EC)DHE public values; HRR names the group the server wants |
signature_algorithms (13) | CH, CR | Algorithms acceptable for CertificateVerify signatures |
signature_algorithms_cert (50) | CH, CR | Algorithms acceptable for signatures inside certificates (if different) |
supported_groups (10) | CH, EE | Groups the client supports (server may list its preferences in EE) |
pre_shared_key (41) | CH, SH | PSK identities and binders; must be last in CH |
psk_key_exchange_modes (45) | CH | psk_ke or psk_dhe_ke |
early_data (42) | CH, EE, NST | Request / accept 0-RTT; max size in NST |
cookie (44) | CH, HRR | Stateless HelloRetryRequest; DoS protection |
server_name (0) | CH, EE | SNI (EE carries an empty ack) |
application_layer_protocol_negotiation (16) | CH, EE | ALPN, now encrypted in the server's answer |
status_request (5) | CH, CR, CT | OCSP staple now rides per certificate in the Certificate message |
signed_certificate_timestamp (18) | CH, CR, CT | SCTs per certificate entry |
post_handshake_auth (49) | CH | Client allows a later CertificateRequest |
certificate_authorities (47) | CH, CR | Hint which CAs are acceptable |
encrypted_client_hello (0xfe0d) | CH, EE, HRR | ECH: the real ClientHello encrypted to the server's public key |
The first governs the live handshake signature (proof of key possession). The second governs what CA signatures the client can verify in the chain. A client might sign-check RSA-PSS in the handshake while accepting PKCS#1 v1.5 signatures in certificates.
In a HelloRetryRequest the server can pack its state into a cookie, forget the connection, and rebuild state when the client echoes it. A return-routability check: spoofed source addresses never see the cookie.
The client offers h2, http/1.1 (or h3 in QUIC); the server picks one in EncryptedExtensions. Strict ALPN enforcement is a defence against cross-protocol attacks (ALPACA).
Lets a server require a client certificate only for sensitive paths, without TLS 1.2-style renegotiation. Not allowed in HTTP/2, so modern designs authenticate the client up front or at the application layer.
The client fetches an ECHConfig from the HTTPS DNS record, encrypts its real ClientHello (with the real SNI) to that key, and wraps it in an outer ClientHello naming a shared front-end. Clients without a config send GREASE ECH so that real ECH traffic doesn't stand out.
TLS Fingerprinting (JA3 / JA4)
Last verified2026-06
What is this?When a client opens a TLS connection, its very first message — the ClientHello — advertises how it wants to talk: which TLS version, which cipher suites, which extensions, which elliptic-curve groups, and so on. Different software builds that list in its own distinctive order. A Python requests script, Chrome, and a piece of malware each produce a recognisably different ClientHello. TLS fingerprinting turns that ClientHello into a short hash so you can identify the client software without decrypting anything.
The key point: the ClientHello is sent in the clear, before encryption starts (it has to be — it's negotiating the encryption). So a network sensor that can't read your encrypted traffic can still read the fingerprint. You're identifying the tool, not the content.
Why it mattersEncryption blinds the defender to payload, but the handshake metadata still leaks. A real browser and a malware C2 (command-and-control) client both speak TLS, but they build their ClientHello differently — so the fingerprint distinguishes "Chrome on macOS" from "Cobalt Strike's default profile" (a commercial attack framework widely abused by criminals) or "a Go program" even though both connections are encrypted. It's a top-of-Pyramid-of-Pain signal: it targets the attacker's tooling, not an IP or hash they can trivially change.
How it works
JA3 (client):  hash of  TLSVersion,Ciphers,Extensions,EllipticCurves,ECPointFormats
               taken from the ClientHello, joined with "-" and "," then MD5'd.

  ClientHello fields ──▶ "771,4865-4866-...,0-23-65281-10-11-...,29-23-24,0"
                     ──▶ MD5 ──▶ e7d705a3286e19ea42f587b344ee6865

JA3S (server): the same idea applied to the ServerHello (version, chosen cipher,
extensions). JA3 + JA3S together fingerprint *both ends* of a session.was published by Salesforce in 2017. Its weakness: it MD5s an ordered list, and TLS 1.3 clients are allowed to shuffle/pad extensions (GREASE values, the padding extension), which makes the raw JA3 unstable and easy to randomise — so a single piece of software can emit many JA3 hashes, and attackers deliberately "JA3-randomise."
(and the JA4+ family, released by FoxIO in 2023) is the modern successor. It fixes JA3's fragility by sorting the cipher and extension lists before hashing (so GREASE/reordering doesn't change the result) and by using a human-readable, structured format instead of one opaque MD5. A JA4 fingerprint looks like t13d1516h2_8daaf6152771_b186095e22b6 — the first chunk is readable (t=TCP, 13=TLS 1.3, d=domain/SNI present, counts of ciphers/extensions, ALPN), the rest are truncated hashes of the sorted lists. JA4+ extends the idea to other protocols: JA4H (HTTP), JA4S (server response), JA4L (latency/location), JA4X (X.509 certificate).
JA4 fingerprint, decoded:
  t 13 d 15 16 h2 _ 8daaf6152771 _ b186095e22b6
  │  │ │  │  │  │       │              │
  │  │ │  │  │  │       │              └─ hash of sorted extensions
  │  │ │  │  │  │       └──────────────── hash of sorted cipher suites
  │  │ │  │  │  └─ ALPN (h2 = HTTP/2)
  │  │ │  │  └──── extension count (16)
  │  │ │  └─────── cipher count (15)
  │  │ └────────── SNI present (d = domain)
  │  └──────────── TLS version (13 = TLS 1.3, read from the supported_versions
  │                extension — not the legacy record version, which 1.3 pins to 1.2)
  └─────────────── transport (t = TCP, q = QUIC)
Security angle
maintain a set of fingerprints for known-bad tooling (Cobalt Strike, Sliver, Metasploit, common Go/Python malware stacks) and alert on them, or invert it — baseline the fingerprints normal in your environment and hunt the rare ones. A ClientHello claiming to be "Chrome" (by User-Agent) whose JA4 matches a Python client is a classic lie-detector for malware and scrapers.
the same trick spots automated clients that forge a browser User-Agent but can't forge the TLS stack underneath — a high-value signal for a consumer app fighting credential-stuffing and scraping. (This is why some bot frameworks now ship full browser TLS stacks specifically to match a real JA3/JA4.)
JA3 is easy to randomise, which is exactly why JA4's sorting matters. Even JA4 only identifies the stack, not intent — a benign tool and malware that both use Go's standard library share a fingerprint, so treat it as one pivot, not a verdict. Combine it with destination, beaconing regularity, and JA3S/JA4S on the server side.
In practiceA JA4 fingerprint is readable in parts — the first section alone tells an analyst a lot before looking anything up:
t13d1516h2_8daaf6152771_02713d6af862
│ │ │ │ │ └─ ALPN: first protocol offered = h2 (HTTP/2)
│ │ │ │ └─── 16 extensions offered
│ │ │ └───── 15 cipher suites offered
│ │ └─────── d = SNI present (a domain name); i = connecting to a bare IP
│ └───────── TLS version 1.3
└─────────── t = TCP (q = QUIC)
then: hash of the sorted cipher list _ hash of the sorted extensions🎯On the job. Fingerprints identify the client software, not the user. Use them to spot a mismatch — a request whose User-Agent claims "Chrome on Windows" but whose TLS fingerprint matches Python's
requestslibrary or Go's HTTP client is a script pretending to be a browser.
Hash-based MAC (HMAC)
What is this?HMAC (Hash-based Message Authentication Code, RFC 2104, 1997) turns any hash function into a MAC: a tag that only someone holding the secret key can produce or check. If the message changes by one bit, or the tag was made with a different key, verification fails.
Why it mattersIt's everywhere a shared secret proves authenticity: AWS request signing (SigV4), webhook signatures (GitHub, Stripe), JWTs with HS256, TLS 1.2's PRF and CBC-suite record MACs, HKDF in TLS 1.3, and one-time codes (TOTP is HMAC over the current time).
How it worksThe naive idea, Hash(key ‖ message), is broken for SHA-256 and other Merkle–Damgård hashes because of length extension (see hashing above). HMAC hashes twice, with the key mixed in differently each time:
HMAC(K, m) = H( (K ⊕ opad) ‖ H( (K ⊕ ipad) ‖ m ) )

ipad = the byte 0x36 repeated to the hash's block size (64 bytes for SHA-256)
opad = the byte 0x5c repeated
  inner hash: absorbs the message under one key variant
outer hash: wraps the inner digest under another, so the inner state is never exposed → no length extension- Security depends on the key staying secret and the hash being a good pseudo-random function. Collisions don't matter much, which is why HMAC-SHA1 and even HMAC-MD5 are not practically broken (but don't choose them for new designs).
- Compare tags in constant time (
hmac.compare_digestin Python,crypto.timingSafeEqualin Node). A normal==stops at the first wrong byte, and the timing difference lets an attacker guess a valid tag byte by byte.
In practiceVerifying a webhook the way GitHub signs it:
import hmac, hashlib
expected = "sha256=" + hmac.new(SECRET, request.body, hashlib.sha256).hexdigest()
if not hmac.compare_digest(expected, request.headers["X-Hub-Signature-256"]):   # ← constant-time compare
abort(401)Key Derivation Functions (KDF)
Last verified2026-10
What is this?A KDF (Key Derivation Function) turns some secret input into keys of the right size and quality. There are two very different jobs hiding under that name:
The output of a Diffie–Hellman exchange is random-ish but not uniformly random and is the wrong size; you need separate keys for each direction and purpose. This should be fast. Tool: HKDF.
Passwords are guessable, so derivation must be deliberately slow and memory-hungry to make each guess expensive. Tools: Argon2id, scrypt, bcrypt, PBKDF2.
| KDF | Full name | Job | How it works | Current guidance (OWASP) |
|---|---|---|---|---|
| HKDF | HMAC-based Extract-and-Expand KDF (RFC 5869, 2010) | Strong secret → many keys | Extract: HMAC with a salt condenses the input into one uniform key. Expand: HMAC with a label ("client key", "server iv") stretches it into as many independent keys as needed | Used by TLS 1.3, Signal, WireGuard, Noise |
| Argon2id | Argon2, "id" hybrid variant (RFC 9106) | Password → hash/key | Fills a large block of memory and reads it in data-dependent and independent passes | Minimum 19 MiB memory, 2 iterations, 1 lane |
| scrypt | — (Percival, 2009) | Password → hash/key | Builds a large table in memory and reads it in a random order | N = 2¹⁷, r = 8, p = 1 |
| bcrypt | Blowfish-crypt (1999) | Password → hash | Repeats Blowfish's expensive key setup 2^cost times | Cost ≥ 10; mind the 72-byte input limit |
| PBKDF2 | Password-Based KDF 2 (RFC 8018) | Password → hash/key | Iterates HMAC many times | 600,000 iterations with HMAC-SHA256 |
Why memory-hard functions matterAn attacker cracking a stolen password database runs thousands of guesses in parallel on GPUs or custom chips (ASICs, application-specific integrated circuits). PBKDF2 needs almost no memory per guess, so parallel hardware makes it cheap. Argon2 and scrypt force each guess to use tens of megabytes of RAM, and memory is far more expensive to parallelise than arithmetic.
In practiceWhat a stored Argon2id hash looks like. Everything needed to verify it is self-describing:
$argon2id$v=19$m=19456,t=2,p=1$c29tZXNhbHQxMjM0NTY$RdescudvJCsgt3ub+b+dWRWJTmaaJObG…   (abridged)
   │       │      │       │  │        │                     └─ the hash itself
   │       │      │       │  │        └─ salt (base64), unique per user
   │       │      │       │  └─ parallelism (lanes)
   │       │      │       └─ iterations (time cost)
   │       │      └─ memory in KiB (19 MiB)            ← raise these as hardware gets faster
   │       └─ algorithm version
   └─ algorithm
Quantum Threat and Post-Quantum Cryptography
Last verified2026-10
What is this?A large enough quantum computer would break today's public-key cryptography. Post-quantum cryptography (PQC) is the set of new algorithms, running on ordinary computers, that are believed to resist quantum attacks. No quantum computer today can break real RSA or ECC keys; the experts' term for one that could is a CRQC (cryptographically relevant quantum computer).
Why it matters nowHarvest now, decrypt later: an adversary can record encrypted traffic today and decrypt it whenever a CRQC exists. Anything that must stay secret for 10+ years (health data, state secrets, long-lived keys) is already at risk, which is why key exchange is being migrated first.
How quantum attacks work, in one line each:
Efficiently factors integers and solves discrete logarithms. Breaks RSA, DH, ECDH, ECDSA and EdDSA completely. Bigger keys don't help.
Speeds up brute-force search quadratically, which roughly halves symmetric security: AES-128 → ~64-bit (borderline), AES-256 → ~128-bit (fine), SHA-256 preimages → ~128-bit (fine). Fix: use 256-bit keys.
The new standards (NIST, August 2024)They rely on different hard problems. The lattice-based ones rest on learning with errors (LWE): solving a big system of linear equations is easy, but if each equation has a small random error added, it becomes infeasible, even for a quantum computer as far as anyone knows.
| Standard | Full name | Former name | Type | Hard problem | Sizes (common parameter set) |
|---|---|---|---|---|---|
| FIPS 203: ML-KEM | Module-Lattice-Based Key-Encapsulation Mechanism | CRYSTALS-Kyber | Key exchange (KEM) | Module lattices (LWE) | ML-KEM-768: public key 1,184 B, ciphertext 1,088 B |
| FIPS 204: ML-DSA | Module-Lattice-Based Digital Signature Algorithm | CRYSTALS-Dilithium | Signatures | Module lattices | ML-DSA-65: public key 1,952 B, signature 3,309 B |
| FIPS 205: SLH-DSA | Stateless Hash-Based Digital Signature Algorithm | SPHINCS+ | Signatures | Only hash-function security | Small keys, signatures of 8–50 KB; very conservative |
| FIPS 206 (in preparation): FN-DSA | FFT-over-NTRU-Lattice-Based DSA | Falcon | Signatures | NTRU lattices | Smaller signatures (~666 B), harder to implement safely |
| HQC (selected March 2025) | Hamming Quasi-Cyclic | — | Backup KEM | Error-correcting codes | A non-lattice fallback in case lattices fall |
KEM vs Diffie–HellmanDiffie–Hellman is symmetric: both sides send a public value and combine. A KEM (key encapsulation mechanism) works like a locked box: the client sends a public key, the server generates a random secret, encapsulates it to that public key and sends back the ciphertext, and the client decapsulates it. Both end with the same secret. TLS 1.3 fits a KEM into its existing key_share messages.
In TLS todaythe hybrid group X25519MLKEM768 (classical X25519 combined with ML-KEM-768) is on by default in Chrome (since Chrome 131, November 2024), Firefox, Safari and major CDNs, so a large and growing share of web traffic is already protected against harvest-now-decrypt-later. It's a hybrid on purpose: the session stays secure as long as either component is unbroken. The key share is about 1.2 KB, which pushes the ClientHello past one packet and has broken a few middleboxes. Post-quantum signatures (ML-DSA) in certificates are not yet deployed on the public web: certificate chains would grow by several kilobytes.
🎯On the job. Start a cryptographic inventory: where do you use RSA and ECC, for what, and how long must the protected data stay secret? Prioritise key exchange for long-lived secrets (enable hybrid groups on TLS terminators and VPNs), keep crypto behind libraries you can swap (crypto-agility), and watch for middleboxes that drop large ClientHellos.
Quick Reference: Where Algorithms Are Used
| Context | Algorithm | Notes |
|---|---|---|
| TLS 1.3 bulk encryption | AES-128/256-GCM or ChaCha20-Poly1305 | Client picks; ChaCha20 for devices without AES hardware |
| TLS 1.3 key exchange | X25519MLKEM768 (hybrid PQ), X25519 or P-256 ECDHE | Hybrid is the browser default since late 2024 |
| TLS certificate signature | ECDSA P-256, or RSA 2048+ (PKCS#1 v1.5 in certs, PSS in the handshake) | Ed25519 certificates exist but browsers don't accept them |
| TLS 1.3 key derivation | HKDF with SHA-256 or SHA-384 | The hash is the one named in the cipher suite |
| SSH bulk encryption | ChaCha20-Poly1305 or AES-GCM | |
| SSH key exchange | sntrup761x25519-sha512 or mlkem768x25519-sha256 (hybrid PQ), curve25519-sha256 | OpenSSH 9.0 (2022) made post-quantum hybrid the default |
| SSH user and host keys | Ed25519 | RSA keys still common; ssh-rsa (SHA-1) signatures disabled since OpenSSH 8.8 |
| GPG / OpenPGP | Ed25519 + Curve25519, or RSA 3072/4096 | |
JWT HS256 | HMAC-SHA256 | Shared secret; verify alg server-side |
JWT RS256 / PS256 | RSA PKCS#1 v1.5 / RSA-PSS, with SHA-256 | |
JWT ES256 / EdDSA | ECDSA P-256 / Ed25519 | |
| Bitcoin, Ethereum | ECDSA on secp256k1 (Bitcoin also Schnorr signatures since 2021) | |
| Signal Protocol | X3DH / PQXDH key agreement (X25519 + ML-KEM), Double Ratchet, AES-256-CBC + HMAC-SHA256 | |
| WireGuard | Curve25519 + ChaCha20-Poly1305 + BLAKE2s | Fixed suite, no negotiation |
| FileVault, BitLocker, LUKS | AES-XTS (128 or 256) | Disk encryption: no integrity tag |
| Password storage | Argon2id (or scrypt, bcrypt; PBKDF2 for FIPS) | Salted; tune the cost to your login latency budget |
| AWS request signing (SigV4) | HMAC-SHA256 | |
| Passkeys / WebAuthn | ECDSA P-256 (most authenticators), Ed25519 |
Interview Questions: Encryption & Cryptography
CBC only provides confidentiality — it chains blocks with XOR and needs a random IV, but it has no built-in integrity, so it's typically paired with a separate HMAC and is historically prone to padding-oracle attacks if implemented carelessly. GCM is an AEAD mode: it encrypts with counter mode and produces an authentication tag in the same pass, so it gives confidentiality and integrity together, and it can authenticate associated data that isn't encrypted. You prefer GCM because it's authenticated by design, hardware-accelerated, and removes the encrypt-then-MAC footguns of CBC. The one rule with GCM is never reuse a nonce with the same key.
It's catastrophic. GCM derives a keystream from the key and nonce, so two messages under the same key and nonce are XORed against the same keystream — meaning the XOR of the two ciphertexts equals the XOR of the two plaintexts, leaking content. Worse, nonce reuse also lets an attacker recover the GHASH authentication subkey, which breaks integrity and lets them forge valid tags for arbitrary messages. So a single nonce reuse compromises both confidentiality and authenticity. The fix is a unique nonce per encryption — a random 96-bit nonce or a non-wrapping counter — or AES-GCM-SIV if reuse is a real risk, since it's nonce-misuse-resistant.
Forward secrecy means a future compromise of the server's long-term private key can't decrypt past sessions, and it requires ephemeral key exchange. TLS 1.2 allowed ephemeral ECDHE but also still permitted RSA key transport, where the client encrypts the session secret to the server's RSA public key — if that key later leaks, all recorded sessions decrypt, so no forward secrecy. TLS 1.3 removed RSA key transport entirely and mandates ephemeral ECDHE for every handshake, so a fresh, discarded key pair protects each session by design. So it's not that 1.2 can't have forward secrecy — it's that 1.2 made it optional and 1.3 made it the only option.
Because TLS 1.3 only supports ephemeral ECDHE key exchange, there's nothing to negotiate about how to exchange keys, so the client sends its ECDHE key share immediately in the ClientHello rather than first asking the server. The server responds with its own key share in the ServerHello, and at that point both sides can derive the shared secret via HKDF, so the server already encrypts the rest — certificate, CertificateVerify, and Finished. The client verifies and sends its Finished, and data flows after one round trip. As a bonus, sending the key share upfront is what lets the certificate be encrypted, hiding it from passive observers, and there's an optional 0-RTT mode that sends early data with the first flight at the cost of replay risk.
ECDSA needs a fresh random nonce k for every signature, and the math is unforgiving: if k repeats across two signatures with the same key, the two signature equations share unknowns and the private key can be solved directly — this is how the PS3 was hacked and how Bitcoin keys have been stolen. Even a slightly biased or predictable k leaks the key over many signatures. Ed25519 eliminates the dependency by deriving k deterministically — it hashes the message together with the private key to produce the nonce — so there's no RNG to fail or repeat, and identical messages produce identical signatures without ever exposing the key. So Ed25519 removes the single most dangerous implementation pitfall of ECDSA.
ECDH is elliptic-curve Diffie-Hellman key exchange; the E on the end, ECDHE, means ephemeral — a fresh key pair generated for each session and thrown away afterward. The distinction matters for forward secrecy. With static ECDH, the same long-term key derives every session secret, so compromising it later decrypts all past traffic. With ECDHE, each session's secret comes from throwaway keys that no longer exist, so a future key compromise can't unlock recorded sessions. That's why modern TLS insists on ECDHE. Mnemonic: the extra E is for ephemeral, and ephemeral is what buys forward secrecy.
Both are deliberately slow, which is the point for password hashing, but bcrypt is only CPU-hard and uses a small fixed amount of memory, so attackers can parallelize it cheaply on GPUs and ASICs. Argon2id is memory-hard — it forces each guess to consume a configurable, significant amount of RAM, which makes massive parallel cracking far more expensive — and the id variant combines resistance to both GPU attacks and side-channel attacks. It also won the Password Hashing Competition and is OWASP's current recommendation. bcrypt is still acceptable, but for new deployments Argon2id raises the attacker's cost more, especially against well-funded hardware. Both must be salted.
Certificate Transparency requires every publicly trusted certificate to be recorded in public, append-only logs, and browsers expect proof of logging, so any issued certificate becomes visible to the world. Domain owners can monitor the logs and detect certificates issued for their domains that they didn't request. The driver was DigiNotar in 2011: that CA was hacked and issued a fraudulent wildcard certificate for Google, which was used to intercept the traffic of hundreds of thousands of users in Iran, and nobody could detect it because mis-issuance was invisible. CT makes that kind of secret mis-issuance immediately detectable, and DigiNotar itself was distrusted and collapsed. The trade-off is that CT publicly exposes all your subdomains.
Shor's algorithm efficiently solves integer factorization and the discrete logarithm problem on a large quantum computer, which completely breaks the asymmetric primitives we rely on — RSA, Diffie-Hellman, ECDH, and ECDSA — because their security rests on exactly those hard problems. Grover's algorithm is a generic search speedup that effectively halves the security of symmetric primitives, so AES-128 drops to about 64-bit security (borderline) while AES-256 stays at a safe 128-bit, and hash collision resistance is similarly halved. The practical implication is that symmetric crypto just needs bigger keys, but asymmetric crypto needs replacing — which is why NIST standardized post-quantum algorithms like ML-KEM (Kyber) and ML-DSA (Dilithium), now being deployed in hybrid TLS.
Because hash functions built on the Merkle–Damgård construction, like SHA-256, are vulnerable to length-extension attacks. The digest of Hash(key ∥ message) is the function's internal state after processing that input, so an attacker who sees the digest — without knowing the key — can resume from that state and compute a valid digest for key ∥ message ∥ extra, forging a MAC for a message they partly control. HMAC defeats this with its nested structure, hashing an inner keyed hash again with the outer key, so the internal state is never directly exposed. So the rule is to use HMAC, or a natively-MAC primitive like Poly1305, rather than naive concatenation.
HKDF is a key derivation function with two stages: extract, which takes input keying material that may not be uniformly random — like a Diffie-Hellman shared secret — and a salt, and condenses it into a uniformly random pseudorandom key; and expand, which stretches that key into as many independent output keys as you need, bound to context labels. TLS 1.3 uses HKDF throughout its key schedule: it feeds the ECDHE shared secret through extract and then derives all the distinct keys the connection needs — separate keys for handshake traffic, application traffic in each direction, exporters, and resumption — each with its own label so they're cryptographically separated. It replaced TLS 1.2's ad-hoc PRF with this clean, analyzed construction.
Certificate revocation checking via plain OCSP has the client contact the CA's responder to ask whether a certificate is still valid, which has two problems: it leaks the user's browsing to the CA, since the CA learns every site you visit, and it adds latency and a hard dependency on the responder being up — many clients "soft-fail" and skip the check if it's slow, undermining it. OCSP stapling moves the work to the server: the server periodically fetches a signed, timestamped OCSP response from the CA and staples it into the TLS handshake, so the client gets fresh revocation proof without ever contacting the CA. That fixes the privacy leak and the latency, and Must-Staple can require it so an attacker can't strip the staple. It's better because it delivers the same revocation assurance without the privacy and availability costs.
It's a hash of the client's ClientHello — the first handshake message, which is sent in the clear and lists the TLS version, cipher suites, extensions, and curves the client supports. Different software builds that list differently, so the fingerprint identifies the client tool without decrypting anything: Chrome, a Python script, and Cobalt Strike each produce a recognisable fingerprint. That's powerful because encryption hides the payload but not the handshake metadata, so a sensor can flag known-bad tooling or spot a connection whose TLS stack contradicts its User-Agent — a browser User-Agent over a Python TLS fingerprint is a classic malware and scraper tell. It's a Pyramid-of-Pain tooling signal, so treat it as a strong pivot, not a verdict.
JA3 MD5s an ordered list of ClientHello fields, but TLS 1.3 lets clients shuffle and pad extensions — GREASE values and the padding extension — so the same software emits many different JA3 hashes and attackers deliberately randomise it, which breaks matching. JA4, from FoxIO in 2023, fixes this by sorting the cipher and extension lists before hashing so reordering no longer changes the result, and it uses a structured, human-readable format instead of one opaque MD5 — you can read the TLS version, SNI presence, cipher and extension counts, and ALPN right off the front. It also generalises into the JA4+ family for other protocols, like JA4H for HTTP and JA4X for certificates. So JA4 is the more robust, less evadable, more readable successor.
TLS gives confidentiality through symmetric AEAD encryption, integrity through the AEAD tag or MAC, server authentication through certificates and a handshake signature, and anti-replay within a connection because every record's nonce includes an implicit sequence number. What it doesn't give is non-repudiation: both endpoints hold the same session keys, so either could have produced any record, and a capture can't prove to a third party what the server said. It also doesn't hide metadata like IPs, timing, sizes or — without ECH — the SNI hostname.
The client builds a path from the leaf through the intermediates the server sent — or ones it caches or fetches via AIA — up to a root in its trust store. For every link it checks the issuer name and key identifier match, the signature verifies with an allowed algorithm and key size, the certificate is within its validity dates, and issuers have CA:TRUE, keyCertSign and respect any path-length and name constraints. Then the leaf-specific checks: the hostname is in the SAN, the EKU includes serverAuth, it isn't revoked, and it carries enough valid CT timestamps. Finally the CertificateVerify signature in the handshake proves the server holds the matching private key right now.
Almost always the server isn't sending its intermediate certificate. Browsers paper over that by caching intermediates from other sites or fetching them via the AIA URL in the leaf, but curl, OpenSSL, Java, Go and most mobile stacks only use what the server sends plus their root store, so they can't build a path. You confirm it with openssl s_client -showcerts and fix it on the server by serving the full chain — leaf first, then each intermediate — rather than by disabling verification in the client.
Forward secrecy means a later compromise of the server's long-term private key doesn't expose past sessions, because each session's secret came from ephemeral Diffie–Hellman keys that were discarded — the long-term key only signed the exchange. RSA key exchange lacked it: the pre-master secret was encrypted to the server's RSA key, so stealing that key decrypts every recording. Session tickets reintroduce the problem quietly: in TLS 1.2 the ticket contains the master secret encrypted under a server ticket key, so whoever steals the ticket key can decrypt every session resumed with it. The fix is rotating ticket keys every few hours and, in TLS 1.3, resuming with psk_dhe_ke so a fresh ECDHE exchange is mixed in.
Because of middleboxes. During deployment testing, firewalls and inspection appliances broke a few percent of connections that showed an unfamiliar version number or message flow, so TLS 1.3 freezes the record and legacy_version fields at 0x0303, negotiates the real version in the supported_versions extension, sends a fake session ID and even a dummy ChangeCipherSpec so the exchange looks like a TLS 1.2 resumption. GREASE adds random reserved values to every list so implementations that choke on unknown values get caught early and the protocol stays extensible.
Three layers. Within 1.3, CertificateVerify signs a hash of the entire handshake transcript, and Finished MACs it, so altering the offered groups or suites breaks verification. Across versions, a 1.3-capable server that ends up negotiating 1.2 or lower writes the sentinel "DOWNGRD" plus a version byte into the last eight bytes of ServerHello.random, which is covered by the signature, so a 1.3 client that sees it knows an attacker stripped supported_versions and aborts. And there's simply less to downgrade to, because the weak suites and groups don't exist in 1.3.
In TLS 1.3 the client guesses a key-exchange group and sends a key share for it in the ClientHello. If the server doesn't accept any of the shares offered — for instance the client sent only the hybrid post-quantum X25519MLKEM768 and the server only supports P-256 — it replies with a HelloRetryRequest naming the group it wants, and the client sends a second ClientHello with the right share. It costs one extra round trip, and the server can include a cookie so it doesn't have to keep state between the two hellos, which helps against DoS.
0-RTT lets a client resuming a session send application data in its very first flight, encrypted with a key derived from the PSK in the session ticket, so a returning visitor saves a whole round trip. The risk is replay: that early data has no fresh server input, so an attacker can capture it and resend it to the same or another server in the fleet, and it has no forward secrecy against the PSK. So servers either reject replays with single-use tickets or ClientHello caches, or — more realistically — only accept idempotent requests in 0-RTT and answer anything else with HTTP 425 Too Early.
It's a chain of three HKDF-Extract steps producing the Early Secret from the PSK, the Handshake Secret from the (EC)DHE shared secret, and the Master Secret. From each stage, HKDF-Expand-Label derives labelled secrets bound to a hash of the transcript so far: early traffic keys for 0-RTT, handshake traffic keys that encrypt the certificate and Finished, and application traffic keys plus exporter and resumption secrets. Traffic secrets are then expanded into an AEAD key and IV, and each record's nonce is the IV XORed with a sequence number. The design gives clean key separation between phases and directions, which is what made it formally analysable.
You either need the session secrets or you need to be in the middle. Clients and many servers can write a key log file when SSLKEYLOGFILE is set, and Wireshark uses it to decrypt TLS 1.2, 1.3 and QUIC. The old trick of loading the server's RSA private key only works for TLS 1.2 RSA key exchange, because there the pre-master secret was encrypted to that key; with ECDHE — and always in TLS 1.3 — the private key only signs, so it reveals nothing about session keys. For production visibility, organisations terminate and re-inspect at a proxy or read plaintext on the endpoint.
CAA is a preventive DNS record saying which CAs may issue for your domain, optionally down to a specific ACME account; honest CAs must check it before issuing, but a compromised or malicious CA can simply ignore it. Certificate Transparency is detective: every publicly trusted certificate must be logged in public append-only logs and carry signed timestamps proving it, so browsers reject unlogged certificates and domain owners can monitor for anything unexpected. You want both — CAA to stop accidental or social-engineered issuance, CT monitoring to catch the cases CAA can't stop.
The log stores certificates as leaves of a binary hash tree and signs the root hash as the Signed Tree Head, which commits to every entry. An inclusion proof shows a certificate is in the tree using only about log2(n) sibling hashes — around 30 for a billion entries — and a consistency proof shows an older tree is a prefix of a newer one, meaning the log only appended and never rewrote history. So a log can't secretly show different contents to different people or remove a mis-issued certificate without auditors noticing.
An attacker in the middle opened their own TLS session to the server and sent a partial HTTP request with no final newline, then forwarded the victim's ClientHello as a renegotiation inside that session. The victim completed a handshake directly with the server, but the server treated it as a continuation of the attacker's connection, so the victim's request — including their cookie — was appended to the attacker's prefix and executed with the victim's authority. The flaw was that the renegotiated handshake wasn't bound to the connection it occurred in; RFC 5746's renegotiation_info fixed that by including the previous Finished values, and TLS 1.3 removed renegotiation altogether.
DV certificates only prove control of the domain, via an HTTP file, DNS record or TLS-ALPN challenge; OV adds verification that the organisation exists; EV adds stricter identity vetting. Browsers check all three identically for the TLS connection — only the name binding is cryptographic. Chrome and Firefox removed the green EV bar in 2019 because research showed users didn't notice when it was missing, and researchers registered companies with colliding names to get misleading EV certificates, so the indicator added cost without meaningfully stopping phishing.
In both, the server sends a CertificateRequest and the client answers with its certificate and a CertificateVerify signature over the handshake to prove it holds the private key. In TLS 1.2 the client certificate travels in plaintext, so a passive observer learns the client's identity, and requesting a certificate mid-connection required renegotiation. In TLS 1.3 the CertificateRequest and client certificate are inside the encrypted flight, and a later request uses post-handshake authentication instead of renegotiation, although HTTP/2 forbids that, so modern designs authenticate the client up front.
An elliptic curve is a set of points with a rule for "adding" two points to get a third; repeating that addition k times from a fixed starting point G gives a public key k·G, and the private key is k. Computing k·G is fast, but going back from the point to k, the elliptic-curve discrete log problem, has no known shortcut much better than about the square root of the number of points, so a 256-bit curve gives 128-bit security. RSA's factoring problem does have clever sub-exponential algorithms, so it needs 3072-bit keys for the same 128 bits, which is why a 32-byte X25519 key does the job of a 384-byte RSA key.
They give the same 128-bit security but come from different worlds. P-256 is the NIST curve: required for FIPS compliance and supported by hardware like smart cards, HSMs, cloud KMS and passkey authenticators, but its constants came from an unexplained NSA seed, which some distrust after Dual_EC_DRBG. Curve25519, as X25519 and Ed25519, has fully justified constants and was designed for fast, constant-time, hard-to-misuse implementations, so it's the default for TLS key exchange, SSH, Signal and WireGuard. secp256k1 is the Koblitz curve Bitcoin and Ethereum chose for efficiency, and you basically only meet it in cryptocurrency. My default is X25519 and Ed25519, and P-256 where compliance or hardware demands it.